Browse categories
Explore
Fiverr Pro
English
$
USD

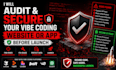


Vibe coded your website or app with Cursor, Replit, Lovable, Bolt, v0, or ChatGPT but not sure if it's actually safe to launch? AI-generated code often ships with hidden security issues: exposed API keys, missing authentication checks, unprotected database rules, or unvalidated user input. I'll review your codebase, find these risks, and fix them before real users (or their payments) touch your app.
What I check for:
Perfect for:
Tech: React, Next.js, Node.js, Tailwind, REST APIs I review code from any AI coding tool, regardless of what generated it.
Message me with your repo/project link and I'll tell you what I find and what it'll take to fix it.
Full Stack Developer, TypeScript, React , Next Js, Express Js
Languages
What is a vibe coding security audit?
I review your AI-generated codebase for common security risks — exposed API keys, missing authentication checks, unprotected database access, and input validation gaps — then give you a report and fix what's found.
My app was built with [Cursor/Replit/Lovable/Bolt/v0] — can you still audit it?
Yes. I review code regardless of which AI tool generated it, since the underlying security issues (exposed keys, weak auth, unvalidated input) tend to be similar across tools.
Do I need to share my source code?
Yes — a repository link (GitHub) or exported project files. Without access to the actual code, I can't run a proper audit.
What if you find a critical issue that could be actively exploited?
I'll flag it immediately, even before delivering the full report, so you can take the app offline or restrict access if needed while the fix is in progress.
Will this guarantee my app is 100% secure?
No audit can guarantee absolute security — new vulnerabilities emerge over time. This audit covers the most common, high-impact risks seen in vibe coded apps and significantly reduces your exposure, but ongoing review is recommended as your app grows.
Do you need admin access, hosting credentials, or API keys?
For a code-only scan (Basic), no — just the repository. For fixes (Standard/Premium), I may need limited access (e.g., a staging environment or specific credentials) depending on what needs to be changed.
What's the difference between Basic, Standard, and Premium?
Basic is a scan + written report only (you fix issues yourself). Standard adds fixes for the top critical issues. Premium includes a full audit, all fixes, and additional hardening like rate limiting and stronger auth checks.
My app isn't launched yet — should I still get this?
Yes, ideally before launch — it's much easier and cheaper to fix security gaps before real users, payments, or data are involved.