Browse categories
English
$
USD
Connect to your AI




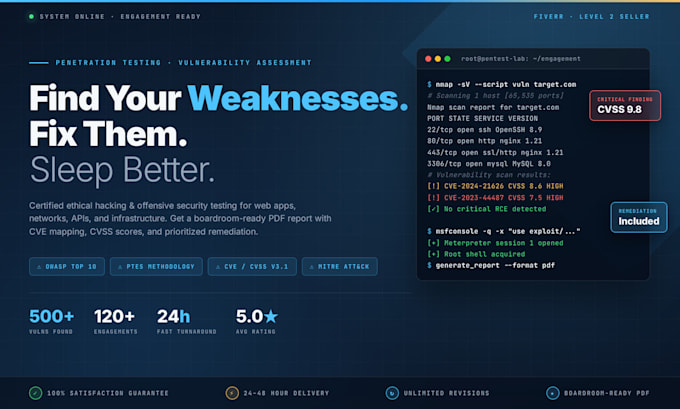
Your web app has vulnerabilities you don't know about. I find them before attackers do.
I'm a cybersecurity specialist performing manual penetration testing not just running automated scanners. Every engagement follows the OWASP Testing Guide and PTES methodology.
WHAT I TEST:
Full OWASP Top 10: SQLi, XSS, SSRF, IDOR, RCE, auth bypass
Business logic flaws automated scanners miss
Session management, JWT, and cookie security
API endpoints (REST/GraphQL) Standard and Premium
File upload, access control, privilege escalation
SSL/TLS configuration and security headers
WHAT YOU GET:
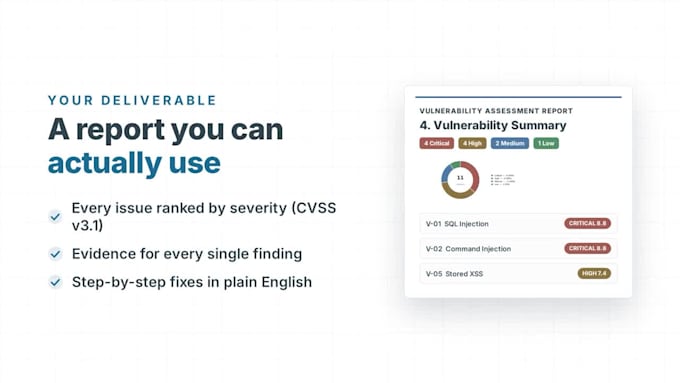
PDF report (15-25 pages) with CVSS v3.1 scored findings
Step-by-step PoC with screenshots for every vulnerability
Developer-ready remediation code snippets
Executive summary for non-technical stakeholders
Free re-test within 90 days of remediation
All testing is 100% safe and non-destructive. Works for staging or production.
WHY ME: Manual testing. Real CVE mapping. Replies in under 5 minutes during business hours.
MESSAGE ME your URL first for a free preliminary scope review. I'll tell you the right package for your budget.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Vulnerability Assessment and Ethical hacking
Languages
Will this pentest take my website down or affect live users?
No. All testing is 100% safe and non-destructive. I never run DoS attacks or destructive payloads. Testing can be scheduled during low-traffic hours or on a staging server.
Do you use automated tools or manual testing?
Standard and Premium packages include deep manual penetration testing using industry tools (Burp Suite, Nmap) and OWASP methodologies to eliminate false positives.
Will you sign an NDA to protect our data?
Absolutely. Strict confidentiality is guaranteed. I am happy to sign your NDA before we begin, and all test data is permanently deleted upon project completion.
Do you offer a re-test after my team patches the bugs?
Yes! Once your developers apply the fixes using my remediation guide, I offer a verification re-test (included in Premium) and issue an updated v2.0 Clean Report.