Browse categories
English
$
USD
Connect to your AI
Is your Security Operations Center delivering measurable security value?
I help CISOs, security leaders, and SOC managers assess SOC maturity, identify operational gaps, and develop practical security operations strategies.
With 20+ years of cybersecurity experience, I provide independent SOC advisory services covering:
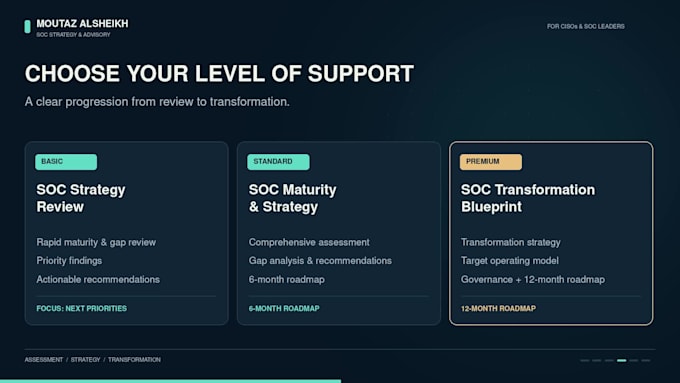
Choose the right engagement:
My approach draws on NIST CSF 2.0, ISO/IEC 27001, and SOC maturity practices.
Services are advisory; hands-on implementation is not included. NDA arrangements can be discussed before engagement.
Contact me before ordering to confirm scope, deliverables, and timelines.

What does this Service provide?
This Service provides a SOC assessment and advisory service to identify gaps, evaluate maturity, and deliver practical recommendations to improve your security operations strategy, processes, governance, and operating model.
What is the difference between Basic, Standard, and Premium?
Basic provides a rapid review and priority findings. Standard offers a deeper assessment with gap analysis and a 6-month roadmap. Premium delivers a broader SOC transformation blueprint with governance, an operating model, and a 12-month roadmap.
Is this service suitable for a new SOC?
Yes. This service supports both existing SOC environments and organisations planning to build or improve a SOC. The assessment and recommendations are tailored to your current maturity and business needs.
Do you implement SIEM, SOAR, or security tools?
No. This Service focuses on advisory, assessment, and strategy. It does not include hands-on implementation, engineering, or tool deployment unless separately agreed as a separate engagement.
What deliverables will I receive?
Depending on the package, you will receive a summary of findings, a gap analysis, prioritised recommendations, and a strategic roadmap. Higher-tier packages may also include governance recommendations and target operating model guidance.
Can you work with an internal SOC or MSSP model?
Yes. I can assess internal SOCs, outsourced SOC models, or hybrid environments. Recommendations will be aligned with your operating model, responsibilities, and business objectives.
Are my documents and internal information kept confidential?
Yes. Client information is treated as confidential and used solely for the agreed engagement. I can also review and sign a mutually acceptable NDA before sharing sensitive information, subject to Fiverr's rules.
Can you customize the SOC strategy to my industry?
Yes. I tailor recommendations to your organisation's size, industry, risk profile, regulatory environment, and business objectives. Contact me before ordering to discuss any specialised or complex requirements.
Do I need to give you direct access to my systems?
No. This engagement typically involves interviews, discussions, and document reviews. I do not require passwords, production credentials, or unrestricted access to your live security environment.
Can this service be used for compliance or audit preparation?
Yes, it can support internal readiness by identifying SOC gaps and areas for improvement. However, this service is advisory and does not replace a formal audit, certification, or regulatory assessment.