Browse categories
Explore
Fiverr Pro
English
$
USD
Elastic SIEM engineer: detection rules, log pipelines, dashboards
Need a SIEM that works in production, not just a lab install?
I run Elastic Security every day in a 24/7 SOC. I will deploy yours the same way: secured, sized for your log volume, and documented.
What you get:
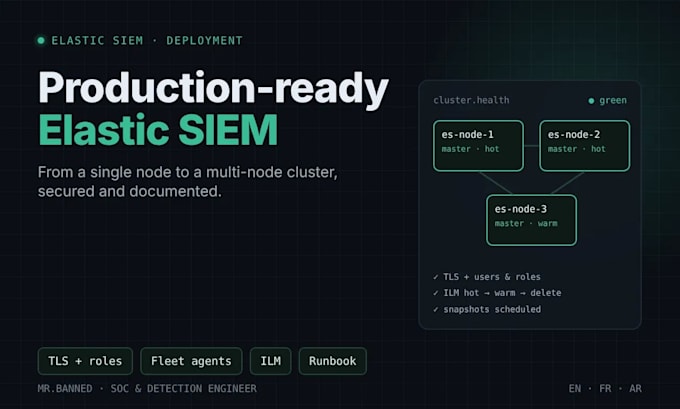
Premium adds a multi-node cluster: dedicated node roles, hot and warm tiers, snapshots.
Why me:
Before ordering, message me your number of hosts, your log sources and where the SIEM should run. I'll confirm the right package and sizing.

Server:
Virtual private server
•
Database server
Operating system:
Windows
•
Linux
Do you need access to my servers?
Yes: SSH or console access to the machines you provide, limited to this project and removed at delivery. If you prefer, I give you the commands and configs and guide you while you run them.
Can you deploy on AWS, Azure, GCP or on-premises?
Yes. Any Linux VM, Docker host or on-premises server. I can also configure an Elastic Cloud deployment you already have.
Which Elastic license do I need?
The free Basic license covers this gig, including Elastic Security detection rules. Some features, such as machine learning jobs and some alert connectors, need a paid subscription. I tell you before we start if your needs require one.
How big should my servers be?
It depends on your daily log volume and retention. Send me your number of hosts and sources and I'll give you a sizing before you order.
What happens after delivery?
You get a runbook and a handover call. If something from my setup breaks within 7 days, I fix it at no cost. Ongoing support is available as a custom offer.
