Browse categories
Explore
Fiverr Pro
English
$
USD
Cloud Architect, DevOps, Intune, SOC and Compliances
Level 1
Has met certain performance criteria and shows strong potential in the marketplace.
Shipping faster should not mean shipping vulnerable code.
I will design or improve a secure Azure DevOps CI/CD pipeline with automated DevSecOps controls. I work with Azure Repos, Azure Pipelines, GitHub Actions, Terraform, Bicep, containers, Azure Container Registry, AKS, and Azure application platforms.
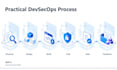
I can implement:
Pull-request validation and branch policies
SAST and CodeQL scanning
Dependency vulnerability scanning
Secret scanning and push protection
Terraform, Bicep, and Kubernetes security checks
Container image scanning
SBOM generation and artifact traceability
Security thresholds and release gates
Workload identity, Key Vault, and least-privilege access
Pipeline documentation and handover
I review your repository, application stack, deployment target, risks, and licensing. I then create maintainable pipeline stages and clear rules for blocking, accepting, or tracking findings.
You receive tested YAML, configuration guidance, security evidence, and documentation from an Azure Cloud Architect.
Please message me before ordering if you need production deployment, self-hosted agents, multiple repositories, AKS, or paid security tools.

Tools:
Docker
•
GitLab
•
Jenkins
•
GitHub
•
Azure Resource Manager
Frameworks:
Npm
•
Terraform
•
Ansible
•
Puppet
•
Other
Programming language:
JavaScript
•
Python
•
PowerShell
Expertise:
Installation
•
Migration
•
Debugging
Can you secure an existing pipeline?
Yes. I can review and improve an existing Azure Pipeline or GitHub Actions workflow. I will identify risky permissions, missing scans, exposed secrets, weak gates, artifact issues, and maintainability concerns.
Do security-tool licenses come with the package?
No. GitHub Advanced Security, commercial scanners, Azure resources, hosted agents, self-hosted infrastructure, and other paid services remain the client's responsibility.
Can you guarantee that the application has no vulnerabilities?
Can you guarantee that the application has no vulnerabilities?
Can you add container and AKS security?
Yes. I can add container builds, image scanning, SBOM generation, registry integration, deployment gates, and AKS-focused controls when included in the package or custom offer.
Will you fix vulnerabilities found by the scans?
The package includes pipeline configuration and reasonable troubleshooting. Application-code remediation, dependency upgrades with breaking changes, penetration testing, and extensive IaC remediation require separate scope.
Can you remove long-lived Azure credentials?
Where supported, I can configure workload identity federation or OIDC and least-privilege Azure RBAC. The final approach depends on your CI/CD platform, deployment target, and organizational policies.


