Browse categories
Explore
Fiverr Pro
English
$
USD
Graduated Computer Science Student
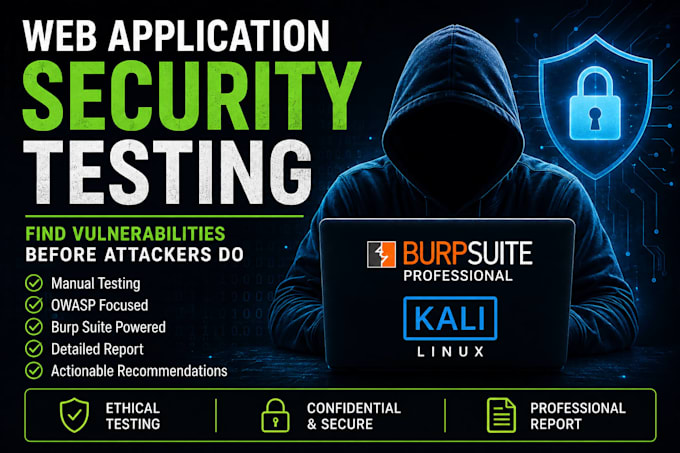
Is your website secure against common web attacks?
I provide authorized web application security testing to help identify vulnerabilities before attackers can exploit them.
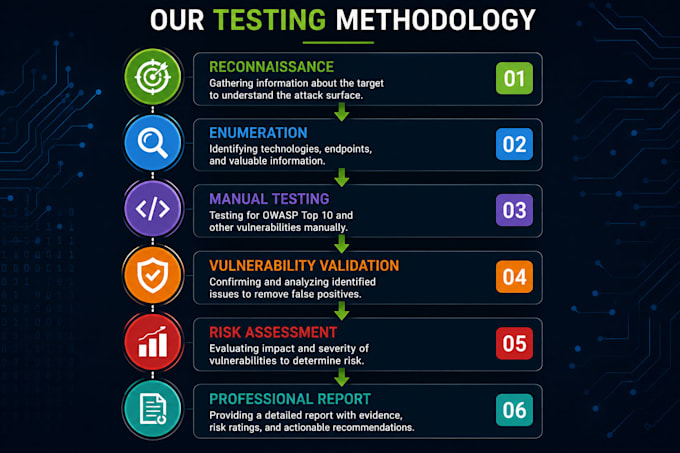
My assessment focuses on common OWASP risks and practical security weaknesses, including:
You will receive clear findings with severity, evidence where applicable, potential impact, and practical remediation recommendations.
What makes my service different:
IMPORTANT: I only test websites, applications, APIs, or systems that you own or have explicit authorization to test. Please contact me before ordering if your scope is unusual or requires authenticated testing.
Let's identify security weaknesses before real attackers do.
Testing application:
Web application
Development technology:
C/C++
•
Java
•
NoSQL
•
Python
•
SQL
Device:
PC
Do you perform unauthorized hacking?
No. I only perform security testing on systems that you own or have explicit authorization to test. The testing scope must be agreed upon before assessment.
What do I need to provide?
You need to provide the target URL/application, testing scope, authorized test accounts if required, and any specific areas you want assessed.
Do you use Burp Suite?
Yes. Burp Suite may be used as part of the manual web application security testing process, together with other appropriate security-testing tools.
Will I receive a report?
Yes. Depending on the selected package, you receive a security assessment report containing findings, severity, evidence where applicable, impact, and remediation recommendations.
Can you test a login-protected application?
Yes, if authenticated testing is included in the selected package and you provide authorized test credentials.
Can you test APIs?
API testing can be provided when the package scope supports it. Please contact me before ordering if your project primarily consists of APIs.
Can you retest after vulnerabilities are fixed?
Yes. Retesting can be included as an additional service or custom offer depending on the scope.