Browse categories
English
$
USD
Connect to your AI
DevSecOps Engineer, Server Hardening, pfSense and Secure CICD
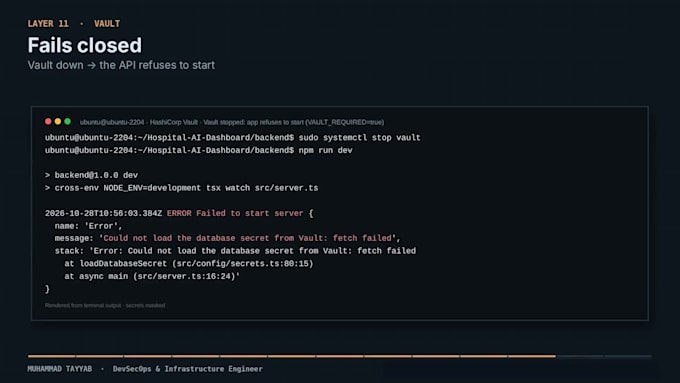
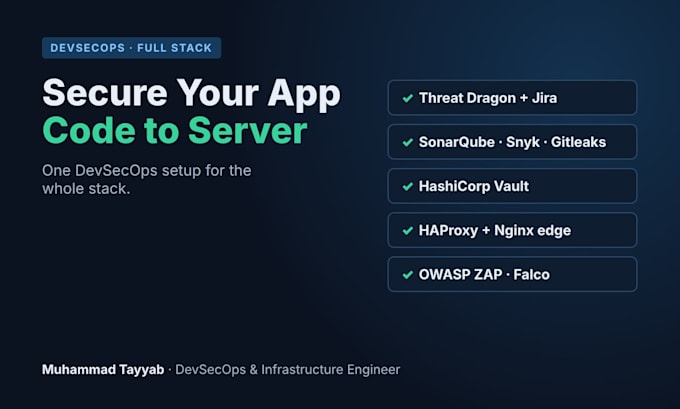
Scanners, bots and leaked secrets are the most common way web apps get hacked. I'll secure your app end to end, from the code in Git to the server it runs on.
What I cover:
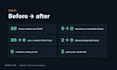
Proof from my portfolio: 69 threats modeled, Snyk 9 to 0, Trivy CVEs 85 to 0, Gitleaks 2 to 0, 13 STRIDE threats fixed on Kubernetes, and a 10-stage DevSecOps pipeline.
I'm a DevSecOps & Infrastructure Engineer running production servers for an EdTech company.
Message me first with your stack so I can suggest the right package.
Tools:
Docker
•
GitLab
•
Jenkins
•
GitHub
•
Hashicorp Vault
Frameworks:
Npm
•
Ansible
Cloud Provider:
Amazon Web Services
•
Digital Ocean
•
VMware Cloud
Programming language:
Bash
•
JavaScript
•
PHP
•
Python
Expertise:
Installation
•
Debugging
•
Configuration
Do I need to change my application code?
Usually no. I only move hardcoded settings like DB host and passwords into environment variables so the same image works on any server. Any small change is explained and shared with you.
What does Trivy scanning do?
Trivy checks your Docker images for known vulnerabilities (CVEs) in the OS and libraries. I fix them by changing the base image, updating packages and removing unused tools, and give you a before/after report.
Can you deploy the containers to my server too?
Yes, in the Premium package. I deploy to your VPS or cloud server (AWS, DigitalOcean, Hetzner, etc.), put Nginx with free SSL in front, and make sure the stack restarts automatically after a reboot.
Do I need all these tools?
No. Start with the Security Audit to see your real risks. I then suggest only the tools you need. All tools I use are free or open-source, so you pay no extra license fees.
Which CI/CD platforms do you support?
GitHub Actions, GitLab CI and Jenkins. Security checks run on every push, and a build fails if a secret leak or critical vulnerability is found.