Browse categories
Explore
Fiverr Pro
English
$
USD


Is your vibe coded app safe to launch? I audit AI-built apps for security holes and fix them, so you don't hear about a leak from a customer.
I'm a full-stack AI engineer and CIO who builds and secures production Postgres, Next.js and Python apps, including LLM and agent features. I read the code and test the logic, not just scan.
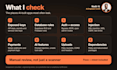
SECURITY CHECKS
BUILT WITH
Lovable, Bolt, Base44, Replit, v0, Cursor, Claude Code, Windsurf, Next.js, React, Supabase, Firebase
YOU GET
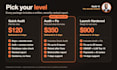
A severity-ranked report, fixes with retest, a before/after summary and a 7-day re-check. Ideal for pre-launch checks, investor due diligence and SaaS MVPs.
Never paste API keys in chat. Not a penetration test or compliance certification.
Software Engineer with Web and AI Expertise
Languages
Is this a penetration test?
No. It's a practical code and configuration review of what most often goes wrong in AI-built apps: keys, auth, database access rules, input handling and payments. It is not a pen test or a compliance certification.
Do you only report, or do you fix?
Quick Audit gives a ranked report and guidance. Audit + Fix and Launch Hardened include the fixes plus a retest. You get a before/after summary of every change.
How is this different from running a scanner?
Scanners catch known patterns. I read the code and test the logic, which is where AI-built apps usually fail: who can read which row, what a logged-out user can call, what a webhook trusts.
Will you access my production data or customer records? A
No. I review code and configuration, and test against staging or a test copy. I never need real customer data.
Do you review AI features such as chatbots and agents?
Yes. Premium includes prompt injection, unsafe tool calls and permission scope, mapped to the OWASP LLM Top 10. It is available as an extra on Standard.
Do you need my passwords or API keys?
No. Add me as a collaborator or share a scoped, revocable key through a safe channel. Any key that has been exposed should be rotated, and I'll flag which ones.
Do you sign NDAs?
Yes. I'm happy to sign one before you share the repo.


