Browse categories
English
$
USD
Connect to your AI
Linux sysadmin for hacked servers, OJS and Moodle
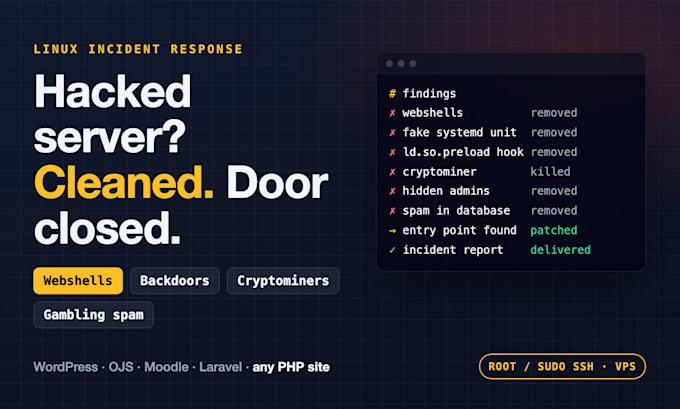
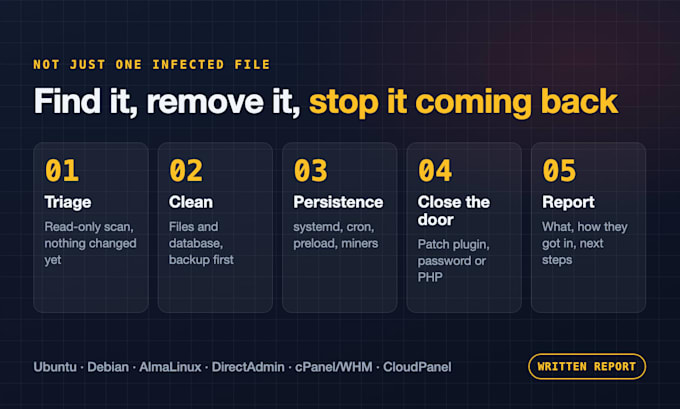
Server slow, sending spam, showing gambling links, or flagged by Google? Cleaning one infected file is not enough - attackers leave persistence behind, and the site gets reinfected next week.
I do incident response the way I do it for my own fleet:
- Find webshells and backdoors in all sites, not only WordPress (OJS, Moodle, Laravel, custom PHP)
- Remove gambling/SEO spam injected into files AND the database
- Hunt root-level persistence: fake systemd services, malicious cron, ld.so.preload, gsocket, cryptominers
- Remove hidden admin accounts
- Find and close the entry point (outdated plugin, weak password, old PHP - upgraded to a patched PHP 8.0 - 8.5)
You receive a written incident report: what was found, what was removed, how they got in, and what to change.
IMPORTANT: root or sudo SSH access is required (VPS, dedicated or cloud server). Shared hosting is not supported.
Not sure how bad it is? Start with the Basic triage - no changes are made to your server.
Operating system:
Linux
Do you work on shared hosting?
Not supported. Root-level persistence (systemd, cron, ld.so.preload) cannot be checked without root or sudo SSH access.
Will my site go down?
Cleanup is done live with backups taken first. Any risky step is discussed with you before I do it.
Do you guarantee no reinfection?
I remove what I find and close the entry point I find; Premium includes 7 days of monitoring. No honest seller can guarantee a server is never hacked again.
Do you take a backup first?
Always, and the backup location is written in the report.