Browse categories
English
$
USD
Connect to your AI
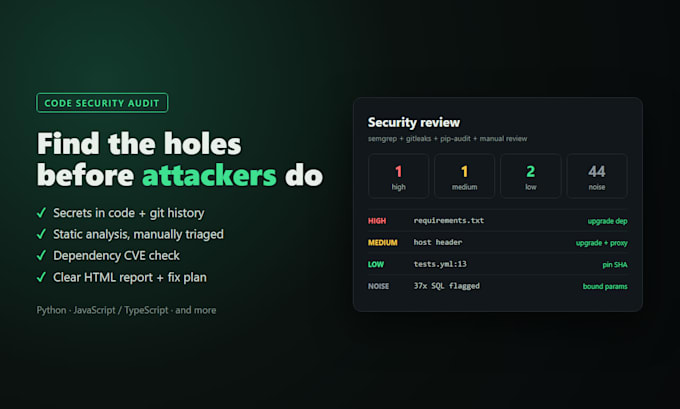
Most teams do not have a security person, but their code still gets attacked like they do. I run a real security review of your repository: secrets in code AND git history, static analysis with manual triage (no scanner dump - every finding is verified in YOUR code), a dependency CVE check, and a clear report your developers can act on.
What you get:
- Self-contained HTML report with severity ratings and reachability analysis
- Prioritized fix plan with concrete remediation steps
- Coverage note showing exactly what was checked and what was not
- Premium: focused fix pull requests, one theme each, with tests
Languages: Python, JavaScript/TypeScript, and most others via scanner rules.
This is a code-level security review, not a penetration test of live infrastructure. A sample report from a published audit of an open-source project is available on request.
Development technology:
Python
Expertise:
Clean Code
•
Design patterns
•
Error handling
•
Unit tests
Will you find every vulnerability?
No honest auditor can promise that. You get a coverage note stating exactly what was checked and what was skipped, so there are no silent gaps.
Do you need production or server access?
No. A repository invite or a zip archive is enough. The review is done on the source code, without touching your live systems.
Is my source code kept confidential?
Yes. The audit runs locally on my machine and your code is not uploaded to third-party services. Happy to sign an NDA, and I delete the copy after delivery.
Can you also fix the issues you find?
Yes, that is the Premium package: focused fix pull requests, one theme each, with tests. You review and merge them - nothing is merged without your approval.
