Browse categories
English
$
USD
Connect to your AI
I will assess your web application and API for security weaknesses using a practical, risk-based approach. My background in Node.js, Python, AWS, and penetration testing helps me review both application behavior and common backend or cloud-related attack paths.
Depending on your package, I can test authentication and authorization, input validation, session handling, API endpoints, business logic, security headers, exposed data, and common OWASP risks.
You will receive:
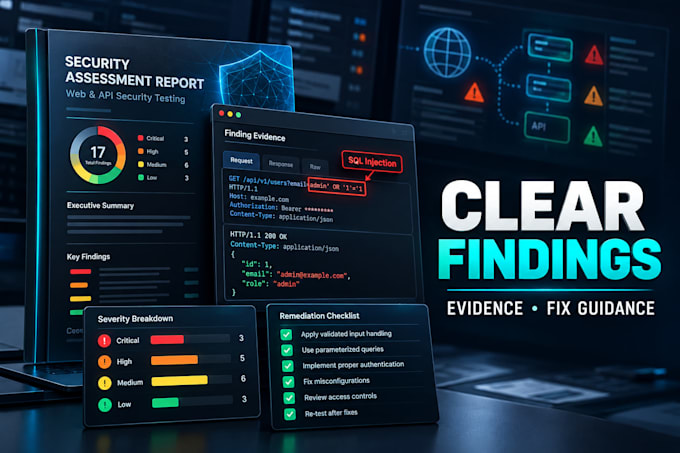
Clear findings ranked by severity
Evidence and reproducible steps
Practical remediation guidance
Annotated screenshots
A concise summary report
Standard and Premium packages include broader functional and browser coverage. Premium adds deeper coverage, performance/load checks, and a retest of reported fixes.
I test only systems you own or are explicitly authorized to assess. Please contact me before ordering if your scope includes many applications, a large API, production load testing, or AWS infrastructure.
Testing application:
Web application
Development technology:
Node.js
•
Python
Device:
PC
•
Mac
•
Linux
Do you require authorization to perform the test?
Yes. I only test systems you own or have explicit permission to assess. You must confirm authorization and the approved scope before work begins.
What access and information do you need?
Please provide the target URLs, in-scope API endpoints or documentation, test credentials when needed, and any exclusions. A staging environment is preferred.
Can you test applications built with Node.js, Python, or hosted on AWS?
Yes. My experience includes Node.js, Python, AWS, and penetration testing. The exact coverage depends on the selected package and agreed scope.
Will this guarantee that my application has no vulnerabilities?
No security test can guarantee zero vulnerabilities. I provide a time-boxed assessment of the agreed scope and practical remediation guidance for confirmed findings.