Browse categories
Explore
Fiverr Pro
English
$
USD
Your Chill Penetration tester
Shipping fast as a solo founder usually means security review gets skipped. That's how exposed API keys, broken auth, and unprotected endpoints end up in production and how one bad actor turns into a data breach, a leaked customer list, or a suspended hosting account.
I'm an eJPT-certified penetration tester with hands-on experience auditing real production systems not just OWASP checklists copy-pasted into a report. I'll test your SaaS, web app, or API the way an attacker actually would, and hand you back a clear, prioritized list of what to fix first.
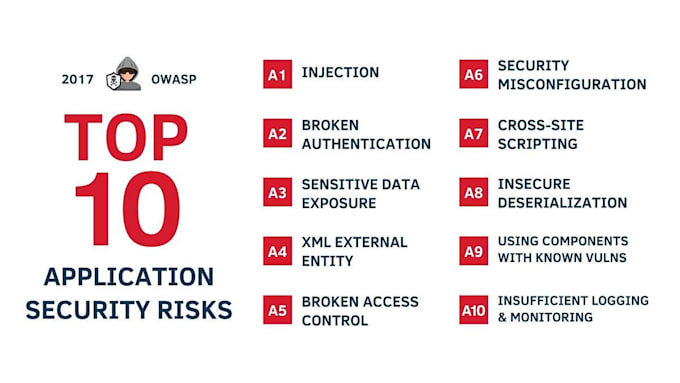
What I check (scoped to your package):
What you get back: A report ranked by severity (Critical / High / Medium / Low), each find


Is this a full penetration test or a vulnerability assessment?
A vulnerability assessment — automated scanning plus manual review to identify and document weaknesses. A full penetration test goes further into active exploitation and social engineering, and is scoped as a custom order.
Will you actually exploit the vulnerabilities you find?
I confirm issues with safe, non-destructive proof-of-concept testing only — no data exfiltration, no destructive actions. The goal is proof the issue exists, not damage.
Do I need to give you production access or credentials?
Staging/test environments are strongly preferred. If production is the only option, testing is scheduled for low-traffic windows and scoped conservatively.
What happens if you don't find any vulnerabilities?
You still get a full report documenting exactly what was tested and confirming those areas are clean — useful for investor due diligence or compliance requirements.