Browse categories
Explore
Fiverr Pro
English
$
USD
Launching an AI-built SaaS (Cursor, Claude Code, Lovable, Bolt, Replit)? Before users, data and payments flow through it, get an independent read-only review of the risks that are easy to miss when you ship fast.
HOW IT WORKS
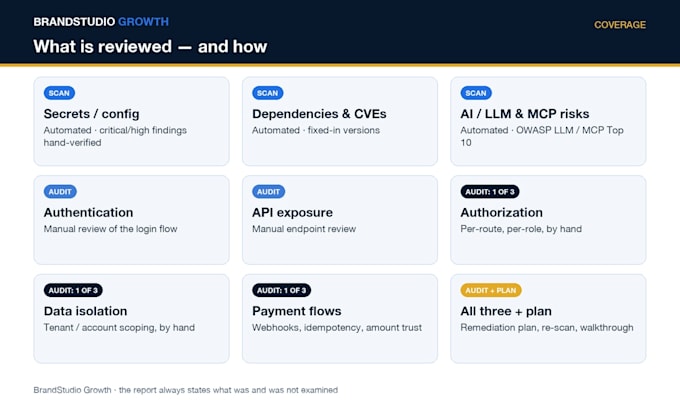
I scan a read-only copy of your code, then manually verify every critical and high finding the scan produces: a prioritised list, not scanner noise.
PACKAGES
Basic: automated scan of secrets and config, dependencies and known vulnerabilities, AI/LLM risks, infrastructure config. No manual review of auth, API or business logic.
Standard: adds manual review of authentication and API exposure, plus ONE of authorization, payment logic or data isolation.
Premium: all three areas, a remediation plan ordered by exploitability and effort, one re-scan after your fixes, a 30-min walkthrough.
PRIVACY
Analysis runs locally; your code is never uploaded to third parties. Offline mode on request. Copies deleted within 30 days.
NOT INCLUDED
Not a penetration test, no live attack testing, not a certification, no guarantee every issue is found.
Automated scanning with human review of every reported finding.
Testing application:
Web application
Device:
PC
•
Mac
•
Linux
•
iPhone
•
Android mobile phone
Is this a penetration test?
No. It is a read-only review of your source code and configuration. Nothing is attacked, exploited or run against your live systems.
What do I need to provide?
A read-only copy of the repository (zip or a read-only repo invite), your stack, and confirmation that you own the code or are authorised to have it reviewed.
Will you test my live app or user journeys?
No. Live journey testing is not included in any package unless agreed separately in writing.
Which package should I choose?
Basic for an automated scan with critical/high findings manually verified. Standard if users log in and call your API. Premium if you have roles/teams, payments and multiple customers' data.
Do you fix the issues?
No — you get locations and remediation guidance (Standard/Premium). You decide what to fix. Premium includes one re-scan after your fixes.
What happens to my code?
Analysed locally, never uploaded to a third-party service, shared with nobody, and deleted within 30 days of delivery (earlier on request).
Can you guarantee my app is secure?
No one honestly can. Automated tools produce false positives and false negatives; the report says which areas were examined and which were not.
My product uses MCP / AI agents — is that covered?
AI/LLM rules run in every package; a dedicated MCP/tool security review is included in Standard and Premium when your product ships MCP.
Does Basic include manual security review?
Only verification of the critical/high findings from the automated scan. Manual review of authentication, API exposure, authorization, payments or data isolation is in Standard (auth, API + one area) and Premium (all).