Browse categories
English
$
USD
Connect to your AI
Lovable, Bolt and Replit apps often go live with the database open: Row Level Security off, or policies that let anyone read other users' data. The app looks fine. The data is public.
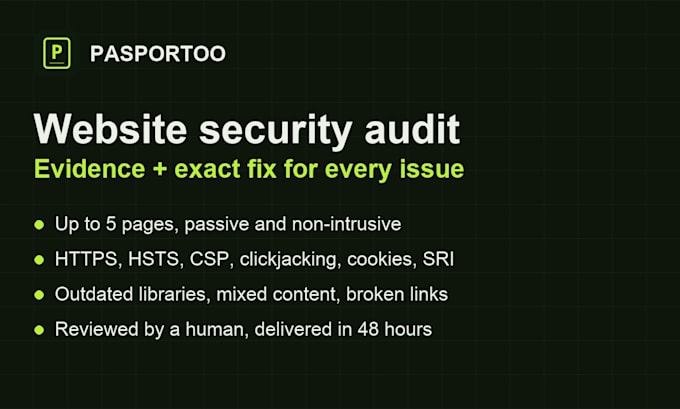
I test your app the way an outsider would, read-only and only with your OK:
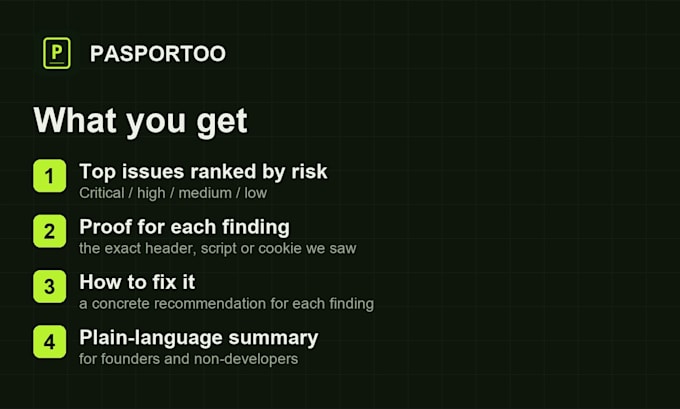
You get a plain-English report and a ready fix for every problem: SQL to paste into Supabase or a prompt for your AI builder. Premium: I write the policies for you and re-test.
No code skills needed. Nothing is changed in your app or database.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Website security audits for startups and dApps
Languages
Is this a penetration test?
Basic and Standard: no, a passive review of what any visitor's browser receives. Premium adds one active test of your Supabase tables, only with your written OK.
Do you need access to my server or code?
No. Just the public URL. If you want fixes applied for you, ask about a custom offer.
Do I need to know how to code?
No. Every issue comes with a ready prompt you paste into Lovable, Bolt, Replit or Cursor, and the AI applies the fix. Stuck? Message me and I will help.
Can I get a re-check after fixing?
Yes, in Standard and Premium.