Browse categories
Explore
Fiverr Pro
English
$
USD
Web Application Penetration Tester Cybersecurity Specialist
Protect Your Web Application with Professional Security Testing
Are you concerned about security vulnerabilities in your website or web application?
I offer authorized Web Application Penetration Testing and Vulnerability Assessment services to help identify potential security risks.
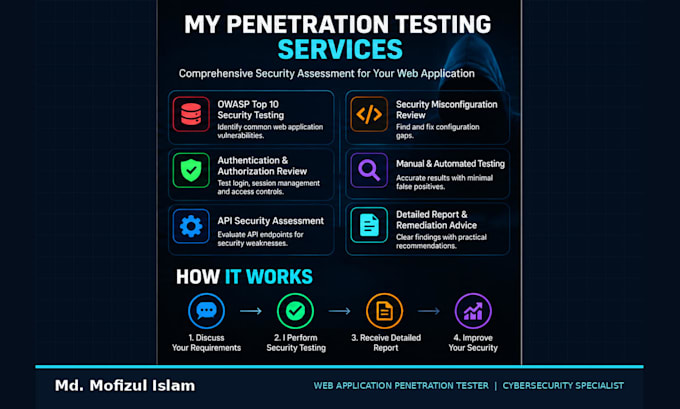
My Services Include:
What You Will Receive:
All testing requires written authorization and an agreed scope. No destructive testing or unauthorized access is included.
Please contact me before ordering to discuss your project scope and requirements.


What is Web Application Penetration Testing?
Web Application Penetration Testing is a security assessment that identifies potential vulnerabilities in websites and web applications. I evaluate security weaknesses based on OWASP guidelines and provide actionable recommendations to improve application security.
What types of vulnerabilities do you test for?
I assess common web application security risks, including SQL Injection, Cross-Site Scripting (XSS), Broken Access Control, authentication weaknesses, security misconfigurations, and other vulnerabilities covered by the OWASP Top 10.
Do you perform manual or automated penetration testing?
I use a combination of manual security testing and automated vulnerability scanning where appropriate. Manual verification helps reduce false positives and provides a more accurate understanding of security risks.
Will I receive a detailed penetration testing report?
Yes! You will receive a professional security assessment report containing identified vulnerabilities, severity ratings, technical explanations, supporting evidence where appropriate, and recommended remediation steps.
Can you test websites built with WordPress, PHP, Laravel, or other technologies?
Yes, I can assess web applications built with different technologies, including WordPress, PHP, Laravel, and JavaScript-based applications, depending on the agreed project scope.
Do you provide OWASP Top 10 security testing?
Yes! My security assessment follows relevant OWASP testing methodologies to identify common web application vulnerabilities and help improve your website's security posture.
Will penetration testing affect my website's performance?
I prioritize controlled, non-destructive security testing to minimize operational risks. However, testing can carry some risk, so I discuss the scope, environment, and testing restrictions before starting.
Do you need access to my website's admin panel?
Not always. I can perform an external security assessment without login credentials. However, authenticated testing may require temporary test accounts to evaluate access controls and protected application functionality.
Can you guarantee that my website will be 100% secure?
No security assessment can guarantee complete protection against every possible vulnerability. My goal is to identify security weaknesses within the agreed scope and provide practical recommendations to reduce security risks.
Why should I contact you before placing an order?
Every website has different features, technologies, and security requirements. Contacting me first allows us to discuss your project scope, testing authorization, timeline, and deliverables so I can recommend the most suitable package.