Browse categories
English
$
USD
Connect to your AI
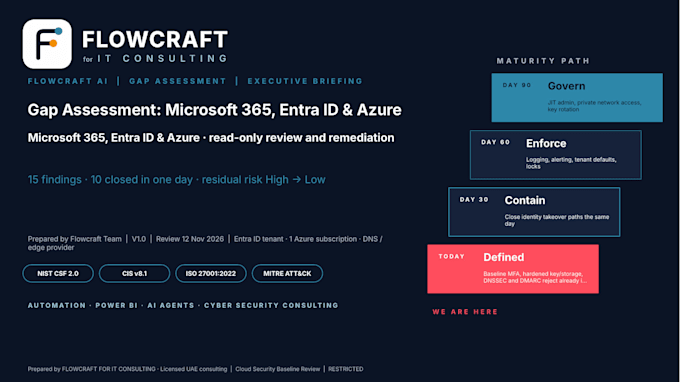
Microsoft 365 and Azure security, Sentinel and automation
Get Microsoft Sentinel working for you, not just ingesting logs.
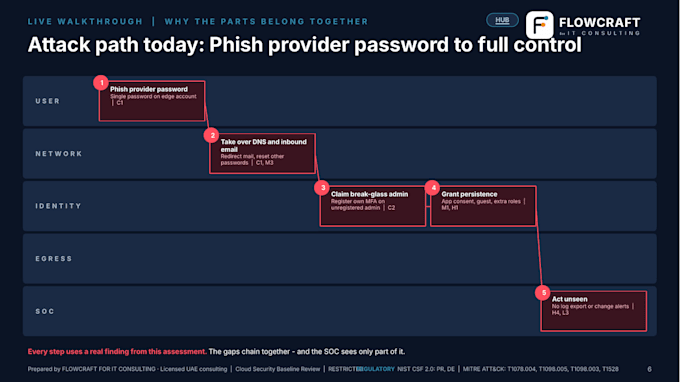
What you get: a configuration report and an ATT&CK detection use-case workbook (log sources, Kill Chain phase, coverage status). Advanced adds Sentinel KQL per use case and HLD/LLD documentation.
Access comes from your own admin, time-limited, with changes only after you approve the plan. Your data stays in your tenant.
Licensed IT consultancy in the UAE, working with clients worldwide.
Not included: 24x7 monitoring or managed SOC. Please message me with your data sources first.


Cloud provider:
Microsoft Azure
Expertise:
Installation
•
Configuration
Cloud computing resource:
Security Groups
Do I need a Sentinel licence?
Sentinel is billed by Azure on ingestion. I review your data sources first and recommend a table and retention plan that keeps cost under control.
Do you provide 24x7 monitoring?
No. I build and tune the detections and playbooks; your team or SOC provider monitors and responds.