Browse categories
Explore
Fiverr Pro
English
$
USD


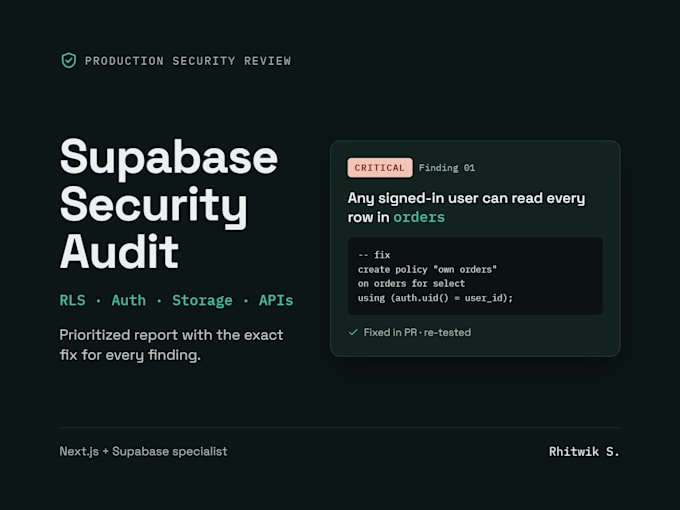
Most Supabase apps ship with at least one table where users can read or change data they shouldnt. The anon key is public by design, so your Row Level Security policies are the only thing protecting your data.
I run production Supabase security audits based on the same 5-phase process I used to harden AhmedSells.ae, a live UAE marketplace I built and run.
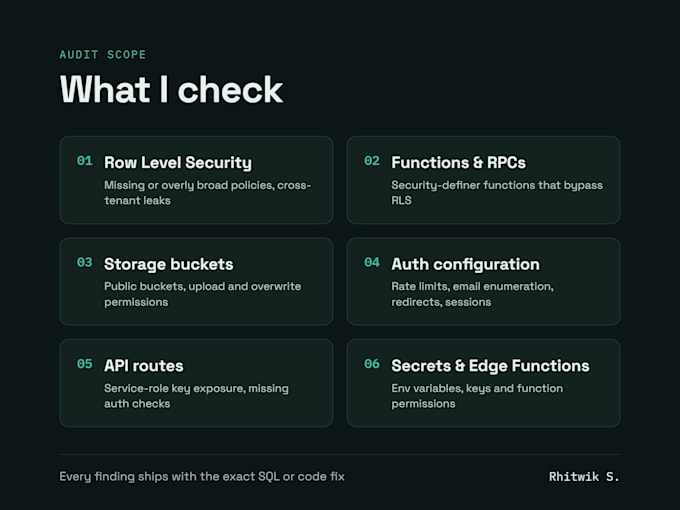
What I check:
RLS policies on every table: missing policies, overly broad USING/WITH CHECK clauses, and cross-tenant leaks
Security-definer functions and RPCs that bypass RLS
Storage bucket policies: public buckets, upload and overwrite permissions
Auth configuration: rate limiting, email enumeration, redirect URLs, and session handling
Next.js API routes and server actions: service-role key exposure and missing auth checks
Edge Functions, environment variables, and secrets handling
What you get: a prioritized report (critical low) with the exact SQL or code fix for each finding, and fixes delivered as a pull request on a separate branch, depending on your tier.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
FullStack Web Developer
Languages
Do you need my production data?
No. Schema, policies, and code are enough. A staging project is ideal.
Do you work with stacks other than Next.js?
The Supabase side works with any frontend. API route checks apply to Next.js.
Will you change anything without asking?
No. All fixes come as a PR for you to review and merge.