Browse categories
Explore
Fiverr Pro
English
$
USD


Every hour your PHP site sits offline or throwing 500 errors, you bleed revenue, SEO rank, and customer trust.
Think a quick PHP version switch fixes everything?
Leading security authorities (CISA/CERT) warn: during critical RCE exposure windows, automated bots quietly plant persistent web shells and hidden cron jobs. Upgrading PHP without auditing core files leaves your back door wide open to repeat attacks.
What I Deliver:
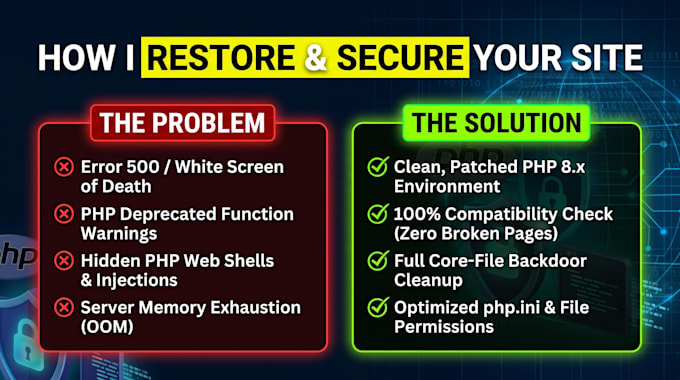
* Zero-Crash Patching: Clean upgrade to secure PHP 8.x without breaking your legacy code.
* Deep Backdoor Sweep: Eradicate hidden web shells, eval/base64 payloads, and rogue scripts.
* Emergency Error Fix: Immediate diagnosis of 500 fatal server logs to restore live traffic.
* Security Hardening: Lockdown upload vectors, file permissions, and php.ini directives.
The "New Seller" Advantage:
High-priced agencies treat you like a ticket queue and overcharge. I am establishing my presence on Fiverr, which means your project gets my obsessive, 100% single-minded focus. My entire platform reputation depends on earning your 5-star reviewgiving you elite cybersecurity rigor at an unbeatable entry rate.
Don't let downtime kill your business. Message me you
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Software Engineer and AI Cybersecurity Specialist
Languages
Will updating PHP break my existing website design or database?
Absolutely not. Before making any changes or touching a single line of code, I take a full manual backup of your files and database. Everything is safely preserved and tested before going live.
What access do you need to start the fix?
I will need temporary access to your hosting control panel (cPanel, Plesk, or DirectAdmin) or FTP/SSH credentials, along with your website URL and error details. FAQ ৩:
Why is a backdoor check necessary after a PHP security update?
Patching PHP only stops new attacks. If your site was exposed to critical vulnerabilities, automated bots often leave hidden web shells and malicious cron jobs behind. My service includes sweeping core directories to ensure no rogue code remains.