Browse categories
Explore
Fiverr Pro
English
$
USD


Launching an app on Supabase (built with Lovable, Bolt, Replit, Cursor or by hand)? Wrong or missing Row Level Security is the most common way these apps leak user data. I make your backend safe to launch, and prove it.
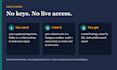
I work from your schema alone: send the supabase/migrations folder or a schema dump (exact steps come with the order). I never need your keys, passwords or live access.
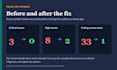
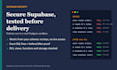
What makes this different: I don't only read policies, I run them. Your schema is loaded into a real Postgres sandbox and tested as a logged-out visitor and as User A trying to read, change, delete or forge User B's rows. You get proof of what the database actually allows, before and after the fix.
You receive:
Checks: RLS off, always-true policies, policies trusting user_metadata, views exposing auth.users, risky SECURITY DEFINER functions, storage policies.
Honest limits: schema-level work, not a penetration test. I use AI-assisted tooling plus my own open-source audit tool, and every fix is re-tested before delivery.
Computer Engineering UG IOT Embedded Systems Engineering
Languages
Do you need access to my Supabase project?
No. I work from your schema only. Nothing connects to your live database.
How do I get my schema?
Use the supabase/migrations folder in your GitHub repo (apps built with Lovable or Bolt usually have one), or run 'supabase db dump --schema public'. I send exact steps after you order.
Will you change my database?
No. I deliver SQL for you to review and apply, ideally on a staging copy first.
How is this different from the Supabase Security Advisor?
The advisor is a good first step. I also run tests as different users against your policies, write fixes that fit how your app works, and re-test them.
Can you guarantee my app is secure?
No one can. This is a schema review with executed tests, not a penetration test.


