Browse categories
Explore
Fiverr Pro
English
$
USD

Level 2
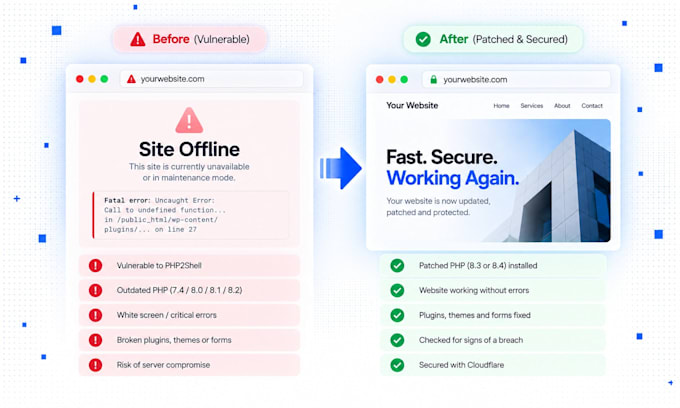
Is your site offline, in maintenance mode or still waiting on a PHP2Shell fix?
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) lets attackers run code on a PHP server without logging in. A WordPress or plugin update does not fix it. Only a patched PHP on your server does, and on a VPS nobody installs it for you.
WHAT I DO:
WORKS WITH:
WordPress, WooCommerce, Laravel, Drupal, Joomla and custom PHP on any VPS, cPanel or Plesk.
YOU GET:
A short report of what I found, what I changed and what to watch next.
PHP 8.2 support ends on December 31, 2026, so this is the right time to move up.
On shared hosting? Your host may already have patched you. Send your URL and host first and I will tell you honestly what you need
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
AI Automation Expert I AI Agents and SaaS Apps
Level 2
Languages
I updated WordPress and my plugins. Am I safe now?
No. PHP2Shell is in PHP, the software under WordPress, so WordPress updates and security plugins cannot fix it. The fix is a patched PHP build on your server plus a restart of every PHP process. I check both.
Which package should I choose?
Basic if your site already runs PHP 8.2 or newer and just needs the patch and a quick fix. Standard if you are on PHP 7.4, 8.0 or 8.1 or your site shows errors. Premium if you run your own VPS or think someone got in. Not sure? Send your URL and I will tell you.
Will updating PHP break my website?
It can, which is why I take a full backup and test before switching. I fix the plugin, theme and custom code bugs the update causes. If a plugin is abandoned, I suggest a replacement before changing your live site.
Can you fix any bug on my website?
Most bugs, yes: critical errors, white screens, broken forms, plugin conflicts and layout issues. Redesigns, new features and custom development are separate work, so message me first and I will quote them.
Can you tell if my site was hacked?
I check logs, new or changed PHP files, scheduled tasks and what your server is running, back to Oct 17 when attacks were first seen. Clean results lower the risk but cannot prove nothing happened, so Premium also resets your passwords and keys.
What access do you need from me?
Your hosting panel login, or for a VPS, a temporary SSH user with sudo. Create a separate user for me and remove it after delivery. I never need your email or payment logins, and I never run exploit code on your server.