Browse categories
Explore
Fiverr Pro
English
$
USD
Cybersecurity Professional Mobile App and Web Pentester
Is your Android application secure?
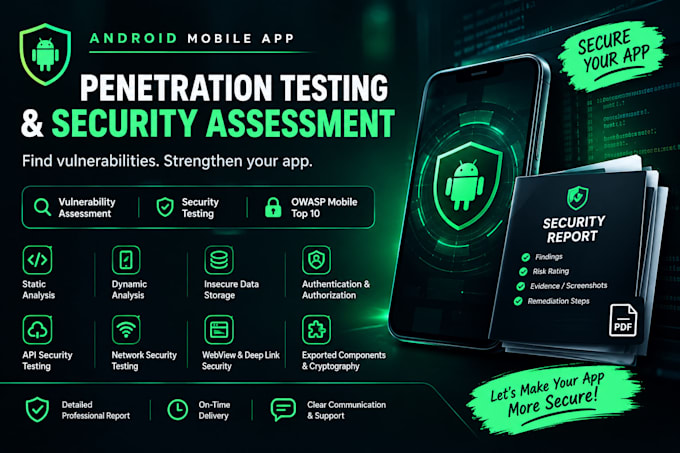
I will perform a professional Android mobile application security assessment to identify vulnerabilities and security weaknesses before they can be exploited.
My testing focuses on both automated checks and manual security testing, based on industry-recognized mobile application security practices.
What I can test:
You will receive:
Testing will only be performed on applications and systems for which you have authorization.

What information do you need to start the security assessment?
I will need the Android APK/AAB file, testing scope, test credentials (if required), API details (if applicable), and any specific areas you want me to assess.
Do you perform manual penetration testing?
Yes. I combine manual security testing with appropriate automated tools to identify vulnerabilities that automated scanners may miss.
What types of Android vulnerabilities do you test for?
I assess areas such as insecure data storage, authentication and authorization, API security, network security, cryptographic weaknesses, WebView security, exported components, deep links, and other common mobile application security risks.
Do you provide a penetration testing report?
Yes. You will receive a professional report containing vulnerability details, severity/risk ratings, technical evidence or screenshots, impact, and recommended remediation steps.
Will you provide Proof of Concept (PoC) for vulnerabilities?
Yes, where applicable and safe to demonstrate. The report will include sufficient technical evidence to help you understand and reproduce the finding.
Can you test both rooted and non-rooted Android applications?
Yes. The testing approach depends on the application and the agreed scope. Some advanced testing may require a controlled/rooted test environment.
Do you retest vulnerabilities after they are fixed?
Yes. A retest can be included depending on the selected package or purchased as an additional service.
Do you test applications without authorization?
No. I only perform security testing on applications for which the client has proper authorization.