Browse categories
English
$
USD
Connect to your AI
Cloud and DevOps Engineer
Need automated, secure, and scalable AWS infrastructure built with clean Terraform code?
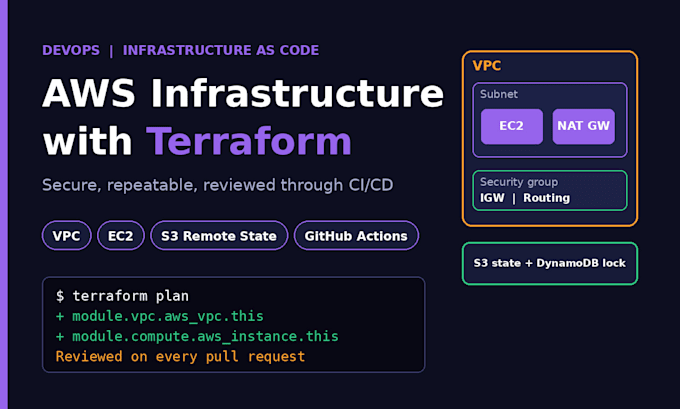
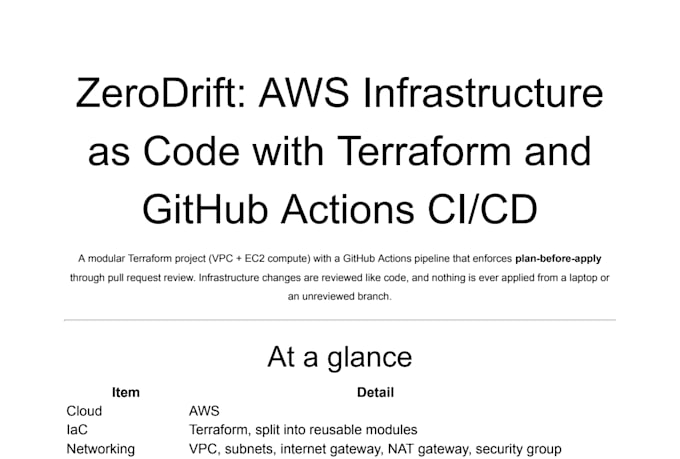
I am a Cloud & DevOps Engineer specializing in Infrastructure as Code (IaC), CI/CD automation, and cloud security. I will design and provision your AWS environment using modular, reusable Terraform configurations so your deployments are repeatable and error-free.
What I Can Build & Automate for You:
Please message me with your project requirements before placing an order so we can align on your architecture and scope!

Cloud provider:
Amazon Web Services
Expertise:
Installation
•
Debugging
•
Configuration
•
Other
Cloud computing resource:
EC2
•
ELB
•
Route53
•
VPC
•
RDS
What do you need from me to get started?
I need your architecture requirements (or existing setup details), your target AWS region(s), and temporary least-privilege IAM credentials - or I can deliver the tested Terraform repository for you to run in your own environment.
Will the Terraform code be modular and reusable?
Yes. All infrastructure is written in clean, well-documented, modular Terraform with separated variables, outputs, and remote state configuration (S3 + DynamoDB) so you can easily scale or replicate environments.
Can you work with my existing AWS infrastructure?
Yes. I can import existing AWS resources into Terraform state, refactor messy configurations, or build new modules alongside your current setup without causing downtime.
Do you include security best practices and CI/CD?
Yes. Every setup follows least-privilege IAM principles and secure networking rules. For Premium orders (or as an add-on), I also configure automated GitHub Actions workflows with Trivy/tfsec security scanning.