Browse categories
Explore
Fiverr Pro
English
$
USD


Get a practical website security check with a short written report and prioritised fixes. Message me your URL and scope before ordering.
BASIC - $15: one website/domain, checking HTTPS/TLS, security headers, cookie flags, visible software disclosure and publicly exposed information. Two-day delivery. This is a limited, non-intrusive review, not a full penetration test or a guarantee that the site is secure. No exploitation, authenticated testing or remediation is included.
STANDARD adds an agreed WordPress/plugin/admin hardening review and SPF, DKIM and DMARC checks. PREMIUM covers an explicitly scoped manual web-app assessment of login, sessions, access control and business logic. Confirm application size and test boundaries before ordering.
My background includes four years of offensive security work for government and defence clients and a First Class cybersecurity degree. Reports combine a plain-English summary with actionable technical findings.
All communication is in writing; no call required. You must own the site or provide written authorisation. Active testing requires agreed scope and permission. No denial-of-service, destructive testing or third-party targets.
Please be aware that it is against Fiverr's policies for sellers to include themes, templates, or any other elements that infringe third-party rights or applicable laws in the delivered work. Read more about in our Guide to Responsible Digital Creation.
Penetration Tester and Cyber Security Engineer, Gov and Defence
Languages
Is this a penetration test?
The Basic package is a passive, non-intrusive check of what your site exposes publicly. Active testing (Premium) only happens with your written authorisation and an agreed scope.
Will the check break or slow down my site?
No. Passive checks look at what your site already serves publicly, at normal browsing speed. Nothing is attacked, and I never do denial-of-service or destructive testing.
Do I need to own the website?
Yes. You must own the site or be authorised by its owner, and I will ask you to confirm this before I start.
What do I get at the end?
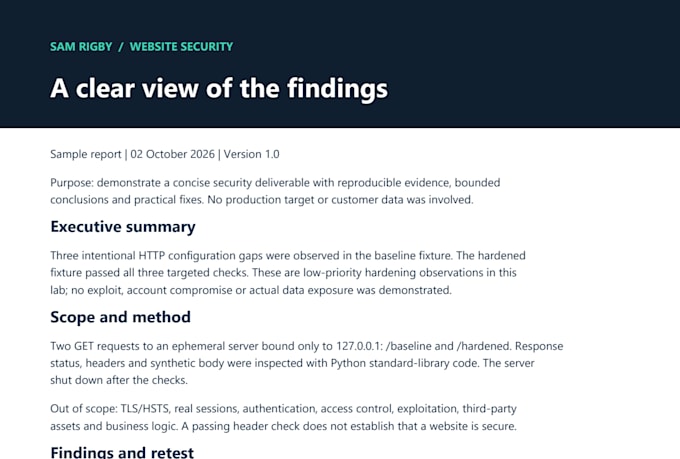
A written report: a plain-English summary, each finding with its risk level, and step-by-step fixes that you or your developer can follow.