Browse categories
Explore
Fiverr Pro
English
$
USD
AI Software Developer for Web Apps, Automation and Code Audits
Get a clear, prioritized view of common risks in your web applications source code before launch.
I will perform one complete static Code Risk Scan of the supported text files in your submitted ZIP. It is designed for TypeScript, JavaScript, React, Next.js, Node.js, SQL, and Supabase projects.
The scan reviews indicators involving exposed secrets, authentication, authorization, APIs, databases, dependencies, deployment configuration, error handling, maintainability, accessibility, performance, testing, documentation, and launch readiness.
You will receive:
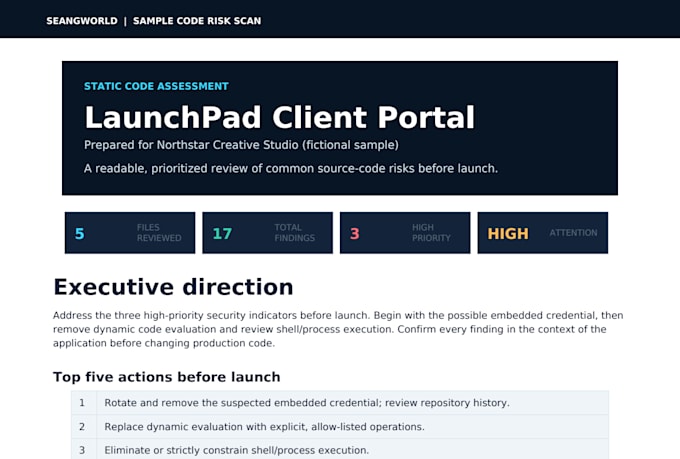
Polished PDF report
Executive summary
Prioritized findings
Top five actions before launch
Remediation roadmap
CSV issue tracker
Project inventory and verification checklist
Scope: One ZIP up to 12 MB and 1,500 files, delivered within one day.
Code is processed as text only. It is not installed or executed. This is not penetration testing, live vulnerability testing, code repair, or security certification. Revisions, fixes, and re-scans are not included.


Testing application:
Web application
Development technology:
JavaScript
•
Node.js
•
React
•
SQL
•
TypeScript
Device:
PC
•
Mac
What types of projects can you scan?
I scan supported text files from TypeScript, JavaScript, React, Next.js, Node.js, SQL, and Supabase web application projects.
Will you install or run my application?
No. Your source code is processed as text only. I do not install dependencies, execute the application, or connect to your live systems.
What will I receive?
You will receive a client-ready package containing a polished PDF report, prioritized findings, top-five actions, remediation roadmap, CSV tracker, project inventory, and verification checklist.
Is this penetration testing or security certification?
No. This is static source-code analysis. It is not penetration testing, live vulnerability testing, compliance verification, or a guarantee that every issue will be detected.
Are fixes, revisions, or re-scans included?
No. This Gig includes one scan of one submitted ZIP. Code repairs, revisions, and scans of corrected or replacement files require a new order.