Browse categories
Explore
Fiverr Pro
English
$
USD
Your contract was audited once, but every upgrade since shipped unchecked. I review each new release of your Solidity code before it reaches mainnet.
WHAT YOU GET
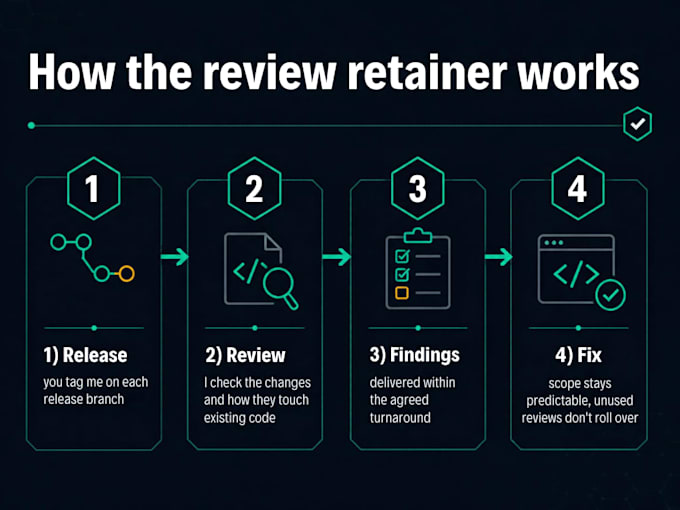
Security review of every change in each release
Slither and Aderyn scans run on the new code
A short written report per review, ranked by severity with fixes
HOW IT WORKS
WHY ME
I built the static-analysis and exploit-testing agents of ASCAS, an AI smart contract auditor (FAST-NUCES final-year project), so I know where scanners miss logic bugs.
WHAT I NEED FROM YOU
Repo access (read-only is enough)
The last audit report, if you have one
Your usual release schedule
Code never audited before? Start with my full Solidity audit gig, then move to ongoing reviews.


Expertise:
Secure tokenization
•
Staking security
•
Privacy
Tools:
MythX
•
Slither
•
Securify
Cryptocurrency services focus solely on developing and programming. Never share sensitive information or private keys with others.
Is this a full audit?
No. It reviews what changed in each release and how that affects existing code. For code never audited before, order the full audit gig first.
How is scope measured?
By lines of Solidity in the contracts you mark in scope. Libraries like OpenZeppelin are excluded unless you've modified them.
Which chains do you support?
Any EVM chain: Ethereum, BNB Chain, Polygon, Arbitrum, Base. No Solana, Move or other non-EVM code.
Does an audit guarantee my contract is safe?
No. It reduces risk by finding and proving the issues present at the commit I review. Code changed after that commit isn't covered.
What's out of scope?
Writing new features, frontend or backend code, deployment, economic or tokenomics design, and code added after the audited commit.
What support do I get after delivery?
You can ask questions about the report for 7 days. Standard and Premium include re-checks of your fixes.