Browse categories
Explore
Fiverr Pro
English
$
USD
Android and iOS Developer, Java, Kotlin, Flutter, Dart, React Native
Is your website, web application, API, server, or system secure against cyber threats? I will perform a professional penetration test and vulnerability assessment to help you identify security weaknesses before they can be exploited.
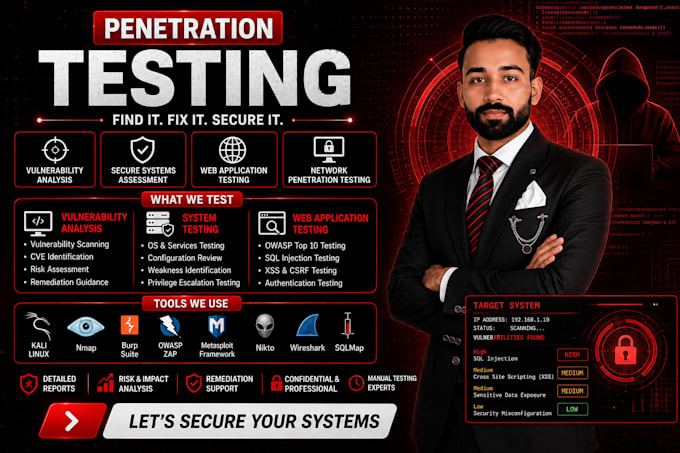
I provide authorized security testing for websites, web applications, APIs, servers, and systems. My approach combines manual testing with industry-standard cybersecurity tools to identify vulnerabilities, validate security findings, assess risk, and provide practical recommendations for remediation.
What I Can Test
Security Testing
Depending on your package and requirements, testing may include OWASP Top 10 testing, vulnerability assessment, authentication testing, authorization testing, session security analysis, input validation testing, security misconfiguration checks, sensitive-data exposure check


Device:
Desktop
•
Laptop
•
Server
Operating system:
Windows
•
Linux
Q: What do you need before starting the penetration test?
A: I need the target URL/IP, testing scope, required credentials (if applicable), and confirmation that you have authorization to test the target.
Q: What can you test?
A: I can test authorized websites, web applications, APIs, servers, and systems depending on the selected package and agreed scope.
Q: Do you use Burp Suite?
A: Yes. I may use Burp Suite along with tools such as Nmap, OWASP ZAP, Nuclei, Wireshark, Postman, and Kali Linux, depending on the target.
Q: Is this a vulnerability scan or a penetration test?
A: The service can include automated vulnerability scanning, but I also perform manual security testing and validate important findings where appropriate.
Q: Will I receive a security report?
A: Yes. The report can include vulnerabilities, severity, evidence, potential impact, and recommended remediation steps.
Q: Can you retest after vulnerabilities are fixed?
A: Yes. Retesting can be included with the applicable package to verify whether reported vulnerabilities have been properly addressed.
Q: Do I need to provide login credentials?
A: Only if authenticated testing is required. Credentials should be provided through a secure method and only for authorized testing.
Q: Can you test a live production website?
A: Yes, if you own the website or have explicit authorization and the testing scope and timing are agreed beforehand.
Q: Do you test third-party websites or systems?
A: No. I only test systems for which the client has proper authorization.
Q: What happens if you find a critical vulnerability?
A: I will document and communicate the finding responsibly, explain its potential impact, and provide appropriate remediation recommendations.