Browse categories
Explore
Fiverr Pro
English
$
USD
Network Penetration Testing | PTES | Nessus Professional
Strengthen your network security before attackers exploit weaknesses.
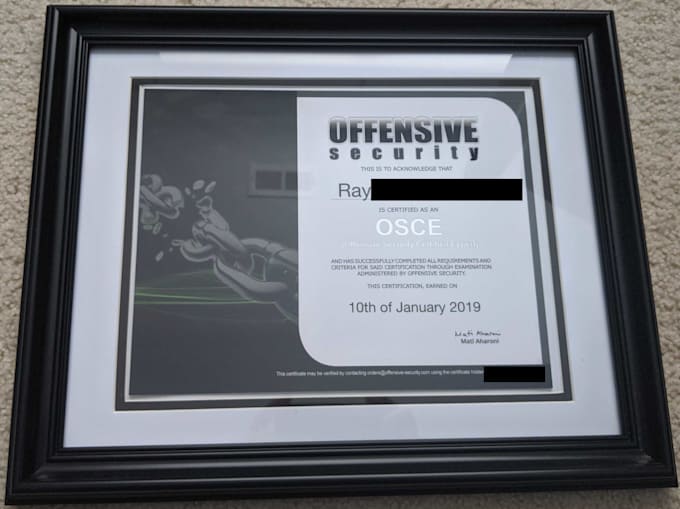
As an experienced and certified Network Penetration Tester, I help organizations identify and fix security vulnerabilities through industry-standard methodologies:
What I Will Do for You
1. Network Reconnaissance & Intelligence Review
2. Full Port Scanning & Service Enumeration
3. Vulnerability Assessment
4. Manual Exploitation Validation
5. Nessus Professional Scan Included
You will receive a detailed professional report with executive summary, technical findings, CVSS v3 severity.

Why do I need a network penetration test?
Networks are often the first entry point for attackers. Pentesting identifies exposed services, misconfigurations, weak credentials, and paths to unauthorized access.
Do you test both internal and external networks?
Yes. External testing simulates real attackers from the internet, while internal testing identifies threats from compromised devices or insider scenarios.
Will my systems or users experience downtime during testing?
No. I perform non-disruptive testing unless explicitly approved for stress or DoS-related checks.
Do you check for vulnerabilities like outdated services or weak protocols?
Yes. I identify outdated software, insecure ports, weak encryption, SMB flaws, and other exploitable weaknesses.
Do you test network devices such as firewalls, routers, and switches?
Yes. I evaluate configurations, access controls, firmware issues, and exposure of management interfaces.
How often should I perform network pentesting?
At least once a year, or after major network changes, new servers, or newly deployed services.
What will I receive after the testing is done?
A detailed report including: • Vulnerability descriptions • Severity classification • Proof-of-Concept where applicable • Clear remediation guidance
