Browse categories
Explore
Fiverr Pro
English
$
USD
Web, Mobile, Blockchain and AI Product Development
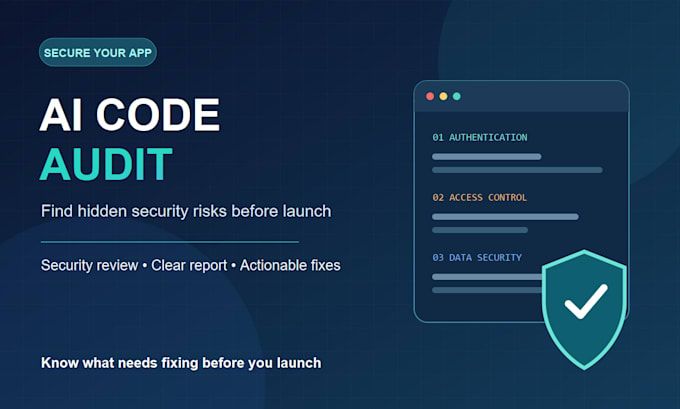
AI-generated code can look ready for launch while hiding security and reliability risks. I review web-app code from Cursor, Claude Code, Lovable, Bolt, Replit or any other workflow and turn findings into a clear action plan.
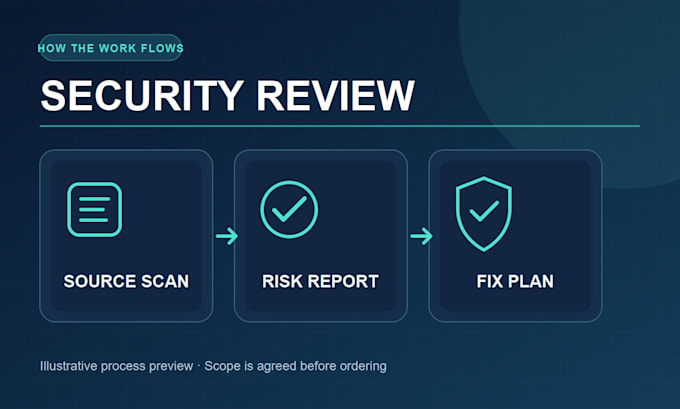
I check authentication and access control, exposed secrets, input validation, injection risks, database permissions, dependencies, configuration and maintainability. Each finding includes severity, file location, impact and a practical recommendation. Manual review is supported by appropriate tools.
Quick Scan covers up to 15 files and critical/high risks. Full Audit covers up to 50 files with a severity-ranked PDF report. Audit + Fixes covers up to 100 files, fixes up to 10 agreed findings and re-checks them. Each package includes one live findings walkthrough: 30 minutes for Quick Scan and Full Audit, 60 minutes for Audit + Fixes. File counts refer to source files; we agree on repo scope before ordering.
SPARK+ Technologies brings 8+ years of software delivery experience. Message me with your stack, repository size and main concern so I can confirm the right package and timeline.
Development technology:
TypeScript
Do you need access to my private repository?
A read-only repository invitation or a code archive is enough. We can agree on access and scope in Fiverr messages before you order.
What is included in Audit + Fixes?
It includes the full audit, code changes for up to 10 agreed findings, and a re-check of those fixes. If the scope is larger, I will propose a separate custom offer before work begins.
Can you audit a project built with Cursor, Lovable or Bolt?
Yes, if you can share the exported source code or repository. Please tell me the framework, approximate source-file count and any deployment or access concerns.
What if the audit finds no critical issue?
You still receive the agreed findings report. I will document the checks completed, any lower-severity risks and practical improvements; a scoped review is not a guarantee that software is risk-free.