Browse categories
English
$
USD
Connect to your AI
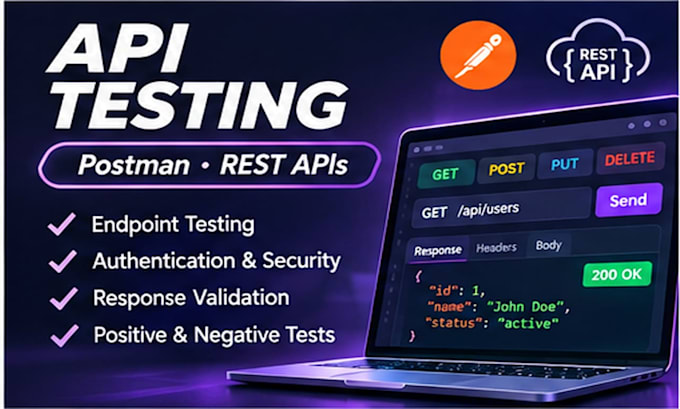
Does your API return the correct responses, handle invalid requests, and enforce expected access rules?
I provide structured REST API testing to help you identify functional issues before they affect your application or users.
I am a QA Engineer with approximately one year of professional experience, including API testing using Postman, Swagger/OpenAPI documentation, and related QA tools.
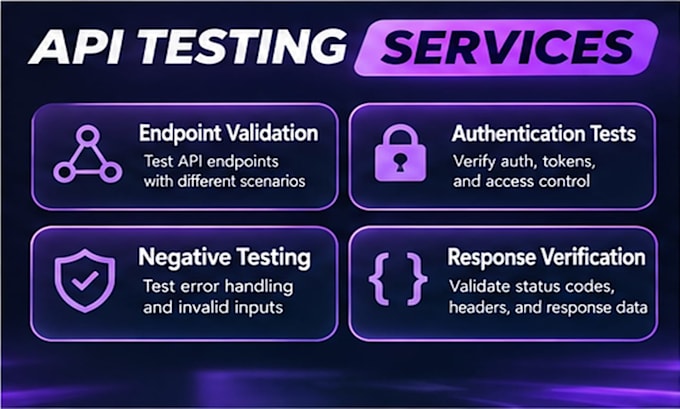
My API testing services include:
What you will receive:
I focus on practical functional testing, clear documentation, and actionable findings.
Please contact me before ordering with your API documentation, endpoint count, authentication requirements, and testing environment so I can confirm the scope and access requirements.
Testing application:
Software
Development technology:
C#
•
Java
•
NoSQL
•
Swift
•
Unity
Device:
PC
What information do you need to start?
Your API base URL, Swagger/OpenAPI documentation or endpoint list, expected responses, and authorized testing access.
Which tools do you use?
Primarily Postman and Swagger/OpenAPI documentation. I also have experience using Burp Suite for request inspection.
What will I receive?
A Postman collection, execution results, documented defects, and a summary of the endpoints and scenarios tested.
Can you test authenticated APIs?
Yes, for supported authentication methods and with suitable authorized test access. Complex identity-provider setups require a feasibility review.
Do you perform security testing?
This gig includes basic negative, authentication, and authorization behavior checks. It does not include a comprehensive penetration test or security audit.
What is excluded?
Load/performance testing, infrastructure audits, API development, production-destructive testing, and complex exploit research are excluded.
How do revisions work?
Revisions cover corrections or clarification of findings and tests within the original scope. New endpoints or requirements are additional work.
Can you provide documentation?
Yes. Reports include endpoint coverage, test outcomes, reproduction steps, and relevant response evidence.