Browse categories
Explore
Fiverr Pro
English
$
USD
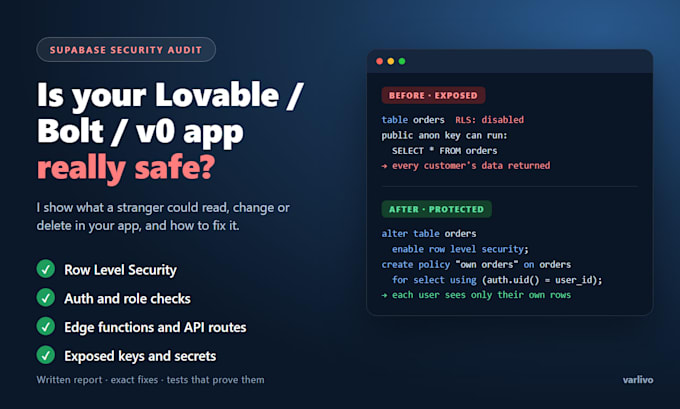
Built your app with Lovable, Bolt or v0? It works, but is it safe? Many AI-built apps ship with open database tables and leaked keys.
I audit your Supabase backend and show what a stranger could read, change or delete.
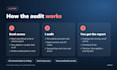
What I check
Row Level Security: missing or wrong policies
Auth and role checks (including client-side-only checks)
Edge functions and API routes without authentication
Secrets and keys exposed in the frontend
User A reading user B's data
What you get
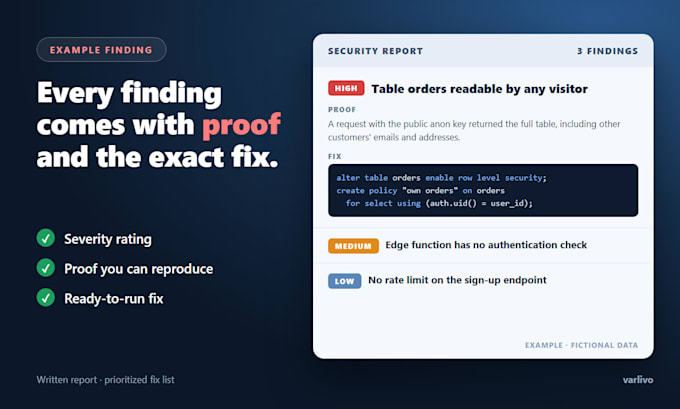
Written report: each finding with severity, proof and the exact fix
Prioritized fix list
Premium: I apply the fixes and add tests that prove them
How I work
All communication is written. I need read-only access, never production secrets, and I test only what you authorize.
This is a security review, not a penetration test, certification or guarantee.
Message me before ordering with your platform and a short app description.
Supabase and full stack developer building secure backends and automations
Languages
Do you need access to my production database?
No. I work from your repository and a schema/policy export, or read-only access to a staging project. Please never send your service role key or production passwords.
Is my code shared with anyone or processed by AI?
Your code is used only for your audit. I use AI-assisted analysis tools, and every finding is verified before it reaches you. If you do not want AI processing, tell me before ordering.
Do you fix the issues?
Basic and Standard include a report and a fix list. In Premium I apply the fixes and add tests that prove they hold.
Which platforms do you cover?
Lovable, Bolt, v0 and any app with a Supabase backend, plus Next.js API routes and security headers.
Is this a penetration test? Can you guarantee my app is secure?
No. It is a security review of what you authorize. It is not a compliance certification, and no review can guarantee that no vulnerabilities remain.
What do I need to provide?
Your platform, a short app description, read-only code or schema access, and your written authorization to test.