Browse categories
English
$
USD
Connect to your AI

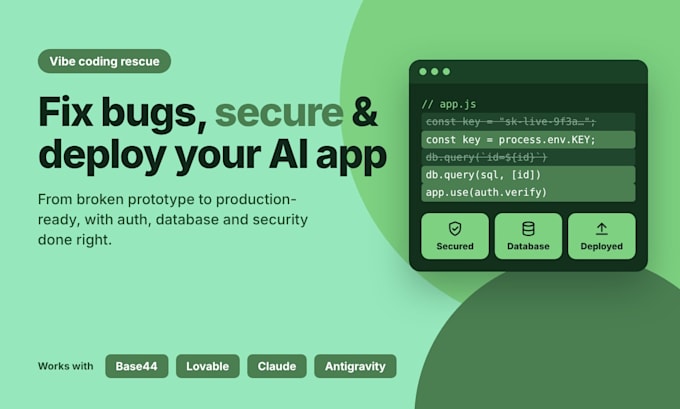
Are you building apps using platforms like Base44, Lovable, Claude, or Antigravity and encountering bugs, database connection issues, or security flaws? I turn AI prototypes into secure, production-ready applications.
What I Offer:
Bug Fixing & Troubleshooting: Resolve logic errors, UI glitches, and broken flows in your AI code.
Database & Auth Integration: Connect databases and configure authentication.
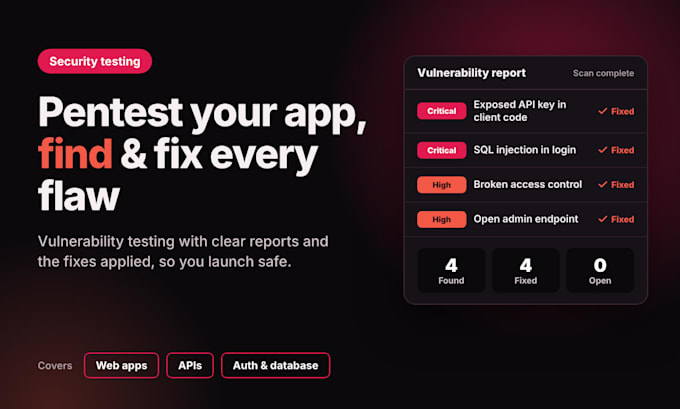
App Security & Hardening: Audit codebases for exposed keys, endpoints, and leaks.
UI/UX Polish: Enhance layout responsiveness and user experience.
Deployment & Setup: Get your app live and ready for users.
Why Choose Me:
Fast turnaround times and clear updates.
Clean code focused on optimization, scalability, and security.
Disclaimer:
I fix existing bugs, logic errors, auth/database issues, and perform pen testing across languages and frameworks (Python, PHP, Java, JS, Flutter, React, etc.). I am not responsible for future flaws, zero-day vulnerabilities, or security issues originating from underlying third-party platforms, frameworks, or language-owning companies.
Message me before ordering to discuss your requirements.
FullStack Developer AI Builder Cybersecurity Enthusiast
Languages
What platforms do you support?
I work with AI app builders and platforms like Base44, Lovable, Claude, and Antigravity.
Do I need to contact you before ordering?
Yes, please message me first to discuss your project requirements and scope.
What languages and frameworks do you handle?
I handle debugging, logic fixes, auth/database setups, and pen testing across frameworks and languages like React, Flutter, Python, PHP, Java, JS, RUST, C++, typescript
Are you responsible for future vulnerabilities?
No. I fix existing bugs, logic flaws, and security issues in your current build, but I am not responsible for future flaws originating from underlying third-party platforms, hosting platforms or frameworks owning-companies.
What happens if a flaw appears after deployment?
If an issue arises from the code fixes I implemented, contact me immediately for review. Issues originating from underlying third-party platforms, frameworks, or language updates are excluded.
Can I use package revisions after the order is marked complete and settled?
No. Standard package revisions only apply during the active delivery and review phase before the order is finalized.
What if a fixed bug resurfaces after deployment?
If a specific bug or logic error I previously fixed fails or resurfaces shortly after completion, reach out so I can review it. New features or separate modifications require a new order.
What are your legal and operational responsibilities regarding future flaws?
I am strictly responsible only for debugging and testing the code within the scope of our order. I hold no liability for future vulnerabilities, updates, or security flaws originating from underlying language owners, frameworks, or third-party platforms.
How do I share my codebase or credentials safely?
Share access via a private GitHub repository or a clean ZIP export. Always provide temporary/test API keys and database credentials rather than master passwords, and rotate your keys once the order is complete.
What does your security audit / pen testing include?
I check for exposed API keys, insecure endpoints, broken authentication/authorization rules, injection flaws, and improper database access controls, then patch the identified vulnerabilities.