Browse categories
Explore
Fiverr Pro
English
$
USD
AI Automation and WCAG Accessibility Engineer
Level 2
Has met high performance criteria and has a proven track record for meeting client expectations.
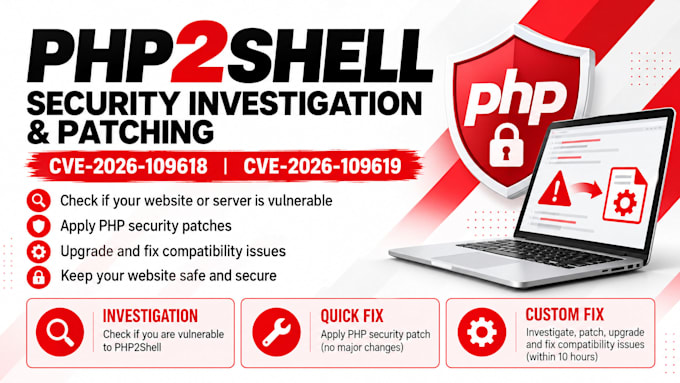
Is your PHP website or server vulnerable to PHP2Shell?
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) involves critical PHP vulnerabilities that may allow attackers to execute malicious code.
I help businesses investigate, patch, and resolve these security risks.
MY PACKAGES
BASIC Investigation (1 Hour)
Check whether your PHP website or server is vulnerable. Receive findings and recommended actions. No fixes included.
STANDARD Quick Fix (2 Hours)
Investigate and apply a compatible PHP security patch without major application upgrades or code changes. Includes basic verification.
PREMIUM Custom Fix (10 Hours)
Investigate, patch, upgrade PHP, and fix application compatibility issues where possible within 10 hours.
SERVICE LIMITATIONS
PLEASE CONTACT ME BEFORE ORDERING to confirm your requirements, compatibility, and scope.
Server:
Apache HTTP
•
Windows server
•
Nginx
•
Web server
•
Other
Operating system:
Windows
•
Linux
•
Unix
What is PHP2Shell, and is my website affected?
PHP2Shell refers to two critical PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619). I can investigate your PHP environment to determine whether it is affected and recommend appropriate fixes.
What is the difference between Standard and Premium?
Standard covers straightforward PHP security updates without major application changes (up to 2 hours). Premium includes up to 10 hours for complex upgrades, compatibility fixes, and custom remediation.
Will my website experience downtime during patching?
Some PHP updates require restarting services, which may cause brief downtime. I will aim to minimize disruption and discuss potential risks before making changes.
What if the vulnerability cannot be fixed within my package?
I will explain the remaining issues and recommend the next steps. Additional work can be arranged through a custom offer. Complete remediation is not guaranteed within the purchased hours.
