Browse categories
Explore
Fiverr Pro
English
$
USD

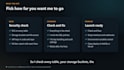
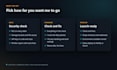

Apps made with Lovable, Bolt or Cursor often work well during demos but can start leaking data once real users show up. Most of the time, the issue is with Supabase: a table with row-level security not enabled, a storage bucket anyone can access, or a secret key that found its way into the browser.
I look for issues manually. I run two live apps on Supabase and Stripe myself (SecPlus Mastery and Keystair). I also have the CompTIA Security+ certification.
What I check:
You get a report in plain English. Each finding tells you what's wrong and how severe it is, with the exact fix (SQL, a setting or a change to your code). On Standard and Premium packages, I handle the fixes and retest them. I work from a collaborator invite and never ask for your passwords. Not sure which package fits? Message me first.
Chrome extensions and launch fixes for apps built with AI
Languages
What do you need from me to start?
The app link, access to the code (a GitHub collaborator invite or a zip file) and an invitation to your Supabase organization. I never need your passwords.
Does the Security check change anything in my app?
No. The check is read-only. You get the report and can apply the fixes yourself, or upgrade to Check and fix.
Is this a penetration test?
No. It is a review of your Supabase configuration, keys and code for the common holes in apps like yours. If you handle medical records or card data, you still need a full penetration test.
My app uses Firebase. Can you help?
The checks are designed around Supabase. Message me first and I will tell you honestly whether I can help.


