Browse categories
English
$
USD
Connect to your AI
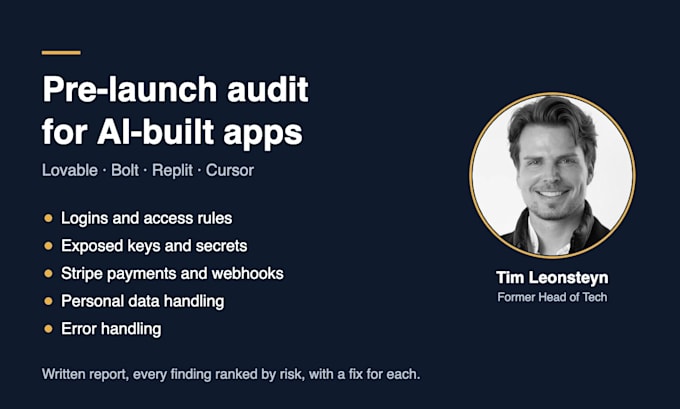
Your app is 80% built with Lovable, Bolt, Replit or Cursor. Before real users and real money touch it, I check the places where AI-built apps usually fail:
- Logins and access rules (Supabase RLS: who can read whose data)
- Exposed API keys and secrets in the frontend
- Stripe payments and webhooks (are failed or repeated payments handled?)
- How personal data is stored and deleted (GDPR basics for EU users)
- What happens when something errors
You get a written report that ranks every finding by risk, with a concrete fix and an effort estimate for each. Fix things yourself, hand the list to your developer, or ask me for a fixed-price quote.
Why me: former Head of Tech (single sign-on, security standards). Today I build and run my own production apps on Next.js, Supabase, Postgres and Stripe.
I need read access to your repository and a staging link. I never need your production passwords.
Rescue and launch audits for apps built with AI
Languages
Do you fix the issues too?
The audit is report only. If you want the fixes done, I quote a fixed price based on the report, and the audit fee is credited when you book the fix.
What do you need from me?
Read access to your repository (for example GitHub), a staging link and a list of the third-party services you use. I never need your production passwords.
Which tech stacks do you cover?
React and Next.js apps with Supabase or Postgres, Stripe and Vercel. Most Lovable, Bolt, Replit and Cursor projects fit. Not covered: native Android, games, blockchain.
