Browse categories
Explore
Fiverr Pro
English
$
USD
Are you looking to secure your infrastructure, analyze suspicious system activity, or triage Security Operations Center (SOC) alerts? I provide professional cybersecurity monitoring and log analysis to identify threats before they impact your business.
Services Offered:
Log Analysis: Deep inspection of Linux, Windows, web server, and network logs.
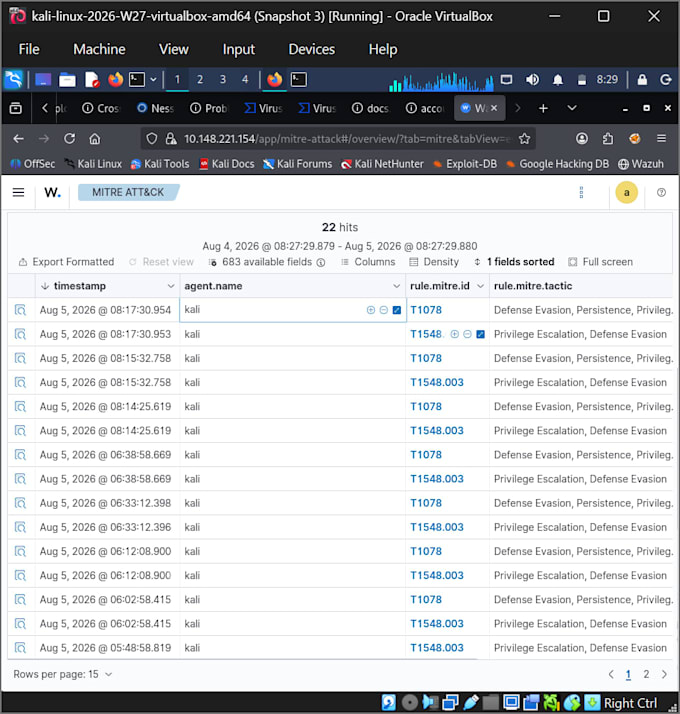
SIEM & Alert Triage: Analyzing alerts (Wazuh, Splunk, Elastic) to differentiate false positives from critical threats.
Incident Analysis: Investigating unauthorized access attempts, malware activity, and network anomalies.
Actionable Reporting: Clear, structured reports detailing identified risks and step-by-step remediation guidance.
Why Choose Me?
Trained in modern cybersecurity operations and network defense.
Practical expertise with SIEM platforms, traffic analysis, and system administration.
Clear communication with non-technical stakeholders and fast delivery.
Note: Please send me a direct message before placing an order so we can discuss your specific technical environment and requirements!


Device:
Desktop
•
Laptop
•
Tablet
•
Router
•
Printer
Operating system:
Windows
•
Linux
•
IOS
•
Android
•
Ubuntu
What log formats do you analyze?
I analyze Linux auth/syslogs, Windows Event logs, web server access/error logs, firewall logs, and SIEM exports (Wazuh, Splunk).
Do I need to share raw system credentials?
No. You can safely send log files (.txt, .csv, .json, .pcap) or grant scoped read-only access to monitoring dashboards.