Browse categories
English
$
USD
Connect to your AI
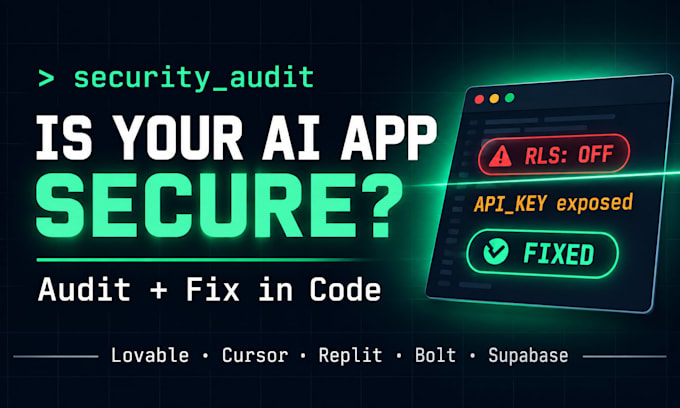
Your app works. But is it safe?
In 2026, a scan of 3,680 Supabase-backed vibe-coded apps found 57% let anyone read their database without logging in. Built with Lovable, Cursor, Bolt, Replit or v0? Yours could be one of them, and attackers check before you do.
One leak can cost you your users, your API credits and your reputation. I find the holes and close them before launch.
WHAT I CHECK
- Exposed API keys and secrets in your code
- Supabase / Firebase RLS and database rules
- Broken login, sessions, JWT and password reset
- SQL injection, XSS, CSRF and IDOR
- Rate limiting, CORS and security headers
- Payment and webhook flows
WHAT YOU GET
- A clear report: every issue, its risk, proof and fix
- Critical issues fixed directly in your code
- Retest to confirm every fix works
- Plain-English summary, no jargon
WHY ME
I'm a full stack developer (React, FastAPI, Python, Supabase) with 3 years in production. I don't just scan and send a PDF. I build apps too, so I fix what I find.
Not sure which package fits? Message me your stack and I'll tell you honestly before you order.
python automation and website developer
Languages
My app works fine. Why do I need an audit?
Working and secure are different. Most leaks happen silently through missing database rules or exposed keys. You won’t notice until someone else does. An audit finds them first.
Is AI-generated code really that risky?
Often, yes. Large 2026 scans of live vibe-coded apps found at least one security issue in 98-99% of them, mostly missing RLS, exposed keys and missing security headers.
Do you need my production passwords or keys?
No. A repo or staging URL is enough. Never send production credentials. If you share any key, rotate it after delivery.
Do you only report, or also fix the issues?
Basic is report-only. Standard fixes all critical and high issues in your code. Premium fixes everything found, hardens the app and retests.
Which tools and stacks do you cover?
Apps built with Lovable, Cursor, Bolt, Replit, v0, Claude or ChatGPT. Next.js, React, FastAPI, Flask, Node, Supabase, Firebase, Vercel and REST APIs.
Can you guarantee my app is 100% secure?
No honest auditor can promise that. I cover the most common and most damaging issues, show proof for each, fix them and retest every fix.
Will you test my live site?
Only apps you own or are authorized to test, using safe, non-destructive checks. Staging is preferred.
