Browse categories
English
$
USD
Connect to your AI
Cyber Security and DevSecOps Engineer
Level 2
Has met high performance criteria and has a proven track record for meeting client expectations.
Most of the incidents I've cleaned up started with something boring: an open security group, an old access key nobody rotated, an S3 bucket someone forgot about, or SSH open to the whole internet.
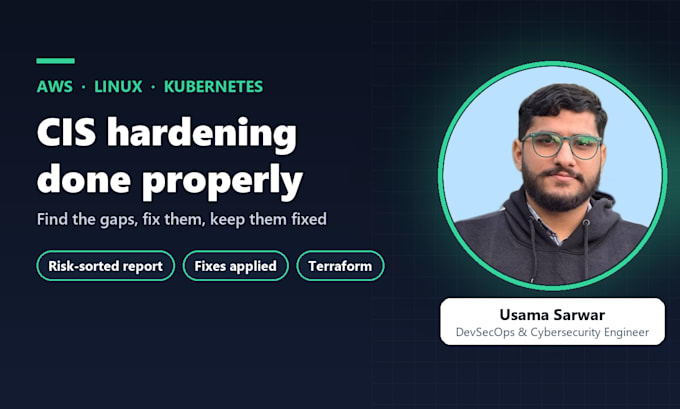
I'll check your AWS account, Linux servers or Kubernetes cluster against the CIS Benchmarks and AWS security best practice, then fix what I find, with your OK first.
You get:
I mostly work with AWS, Ubuntu, Amazon Linux, RHEL, Docker and Kubernetes.
Please don't send passwords or keys in chat. I'll explain how to give me safe, limited access before we start.
Tools:
Docker
•
GitLab
•
Jenkins
•
GitHub
•
Maven
•
Kubernetes
•
OpenShift
Frameworks:
Npm
•
Terraform
•
Ansible
•
Chef
•
Puppet
Cloud Provider:
Amazon Web Services
Programming language:
Bash
•
Java
•
Python
•
Golang
Expertise:
Installation
•
Debugging
•
Configuration

Social Media
I worked as the discord manager for the productivity cafe and establish a completely new discord server for them as well.
Jan 2024

PBS Engineers
Mechanical Engineering
I have created a notion template for PBS Engineers so that I can shift the whole workspace on notion
May 2025
Do you need full admin access?
No. For the audit, read-only access is enough, for example an AWS SecurityAudit role. If you want me to apply fixes, we agree a limited role first.
Will hardening break my app?
I roll changes out in small steps and check the app after each one. Anything risky, like closing a port your app uses, waits for your sign-off.
Which CIS level do you follow?
Level 1 by default, because it's safe for most production systems. I can go to Level 2 if your compliance needs ask for it.
