Browse categories
Explore
Fiverr Pro
English
$
USD


Multi-tenant data isolation is one of the easiest things to get subtly wrong in a SaaS app. "RLS is enabled" is not the same as "tenant isolation is proven" and the gap between those two claims is where real security bugs hide.
I implement and test PostgreSQL Row-Level Security policies for your Supabase/Postgres schema so Organization A genuinely cannot access Organization B's data not assumed, tested. I check against direct resource-ID access, cross-tenant queries through API endpoints, and other common edge cases that basic RLS setups miss.
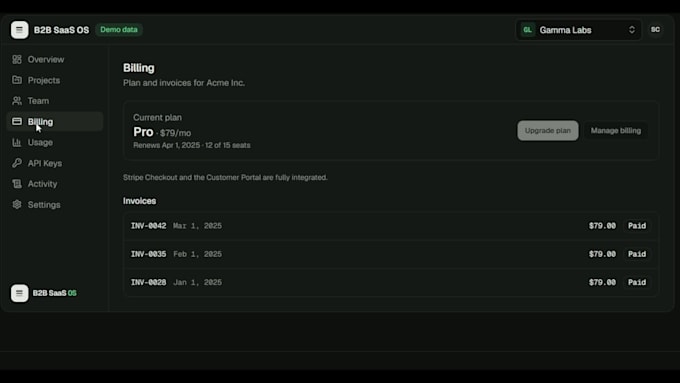
Recently built a full production-ready multi-tenant SaaS foundation from scratch in 26 hours, verified against 26 separate production checks covering auth, tenant isolation, billing, and API security.
What you get: RLS policies written for your actual schema, a test suite proving isolation holds under real access attempts, and a written summary of coverage and any remaining gaps.
Stack: Next.js, Supabase, PostgreSQL, TypeScript.
Message me before ordering if your schema has unusual requirements happy to scope it first.
Backend infrastructure for B2B SaaS: auth, RLS, billing
Languages
What if I don't have Supabase set up yet?
That's fine — I can set up your initial schema alongside the RLS policies. Just mention this when you order so I can scope it correctly.
How do you actually test that isolation works?
I write test queries that simulate a user from one organization trying to access another organization's data directly — through the database, not just through your app's UI — and confirm they're correctly blocked.
Do you only work with Supabase, or plain PostgreSQL too?
Both. Supabase is built on PostgreSQL, so the RLS approach is the same — I just also handle Supabase-specific pieces like Auth integration where relevant.
What's not included?
This gig covers RLS policy implementation and testing. It doesn't include unrelated backend work, frontend changes, or Stripe/billing integration — that's covered by a separate gig if you need it.