Browse categories
Explore
Fiverr Pro
English
$
USD


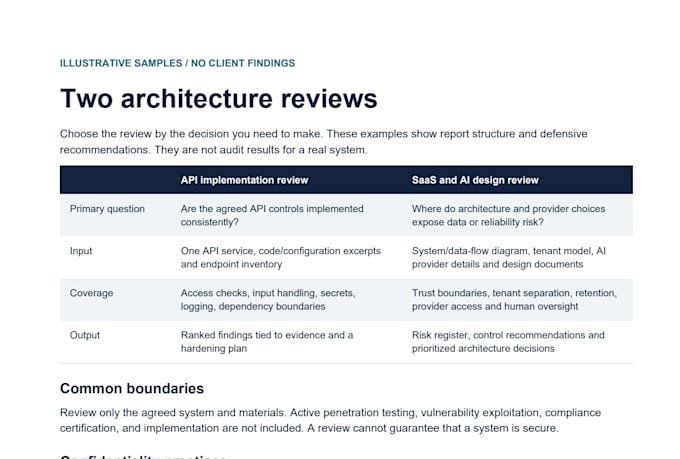
Choose this review when you need to assess an existing API implementation. I review the agreed code, configuration, and endpoint flows for access-control, input-handling, secrets, logging, and dependency risks.
The Basic review is limited to one API service and its agreed flows. Broader tiers cover the service set agreed before ordering. You receive ranked findings tied to evidence, recommended controls, remediation priorities, and acceptance checks.
For system diagrams, tenant design, AI providers, and data retention decisions, choose my separate SaaS and AI architecture review.
I confirm scope and evidence at kickoff, update you at least every two business days during active work, and provide a written handoff. Remediation is separately scoped.
Use sanitized materials and scoped read-only access. We agree permitted tools, retention, and deletion; access is revoked at handoff. The gallery contains illustrative samples, not client findings.
No penetration testing, exploitation, compliance certification, legal opinion, or security guarantee is included.
API and SQL Performance, Integrations and Production Reliability
Languages
Will you recommend a rewrite?
Only if evidence supports it. The preferred outcome is usually the smallest credible path that reduces risk and improves delivery, including incremental modernization where appropriate.
Is this a security audit?
Yes. I review the agreed API architecture and code for security risks and provide ranked findings and a hardening roadmap. This does not include penetration testing, compliance certification, or a guarantee of security.
How much of the codebase will you review?
Representative areas agreed during discovery. Exhaustive line-by-line review of every application, service, and repository is excluded unless separately scoped.
Who should join discovery?
Ideally one technical owner and one business stakeholder who can explain priorities, constraints, and past decisions.