Browse categories
English
$
USD
Connect to your AI

Is your Supabase application properly protecting your users' data?
If you're building a SaaS application with Supabase, incorrect Row Level Security (RLS) policies can expose sensitive customer data or allow unauthorized users to access records they don't own.
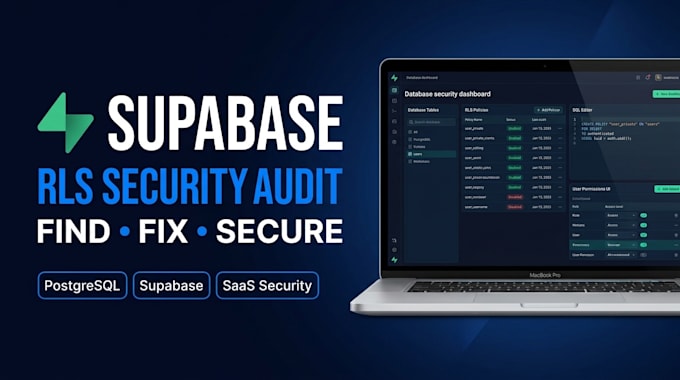
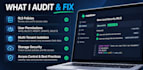
I will review your Supabase database security, test access permissions and help identify and fix RLS vulnerabilities.
WHAT I WILL REVIEW:
WHAT YOU WILL RECEIVE:
WHY WORK WITH ME?
I'm a Full-Stack Developer experienced in Next.js, React, Node.js, PostgreSQL and Supabase.
I've built EverlearnAI, an AI-powered learning and testing platform using Next.js, Flutt
CEH Certified Full Stack Developer SaaS AI and Backend
Languages
What is Supabase Row Level Security?
RLS is a PostgreSQL security feature that controls which database records users can access or modify based on authorization rules.
Can you fix existing RLS policies?
Yes. I can review existing policies, identify issues, implement agreed fixes and retest access permissions.
Can you secure a multi-tenant SaaS application?
Yes. I can review tenant isolation and test whether users from one organization can access another organization's records.
Do you review Supabase Storage?
Yes, Storage policies can be included in the Premium package.
Do you need access to my production database?
Not necessarily. I prefer a development or staging environment with limited permissions. Schema exports and policy definitions can be used for an initial review.